Compare commits
| Author | SHA1 | Date | |
|---|---|---|---|
 fen |
0ceeabc810 | ||
|
fen
|
aca99bc6d4 | ||
|
fen
|
073d39ccba | ||
|
fen
|
9ec7d5152e | ||
 fen |
a677e627a8 | ||
|
fen
|
7a2fa00f4a | ||
|
fen
|
6b95994c53 | ||
|
fen
|
7fde147500 | ||
|
fen
|
cf8674b898 | ||
|
fen
|
f6e81de2a3 | ||
|
fen
|
e17ea4f8c2 | ||
|
fen
|
5afe81f34c | ||
 poslop |
097ffb7971 | ||
|
poslop
|
815635a973 | ||
|
fen
|
df73d56e32 | ||
|
fen
|
9d89995c91 | ||
|
fen
|
805cc3ff2b | ||
|
poslop
|
f37cc932c4 | ||
 agent |
65ed0c7043 | ||
|
poslop
|
8ecf5338d5 | ||
|
poslop
|
69da340224 | ||
|
poslop
|
b1af398bea | ||
|
poslop
|
15f199b2fe | ||
|
poslop
|
9df6224a27 | ||
|
poslop
|
c35531e03e | ||
|
poslop
|
be2b4fb47f | ||
|
poslop
|
064f05536a | ||
|
poslop
|
4175ffef3e | ||
|
poslop
|
ea9edc211a | ||
|
poslop
|
6d467312af | ||
|
poslop
|
b21be29daa | ||
|
poslop
|
cd70dd0b0e | ||
|
poslop
|
ffc10c2b86 | ||
|
poslop
|
bf5a79878f | ||
|
poslop
|
60200ac14b | ||
|
poslop
|
49f7b6e7a4 | ||
|
poslop
|
959a83be1e | ||
|
poslop
|
5b068faf8f | ||
|
poslop
|
b0360af79c | ||
|
poslop
|
806798fae6 | ||
|
poslop
|
8977c05cda | ||
|
fen
|
389e4d333f | ||
|
fen
|
99a044e8a2 | ||
|
agent
|
3d1d5ee1fd | ||
|
Hermes Agent
|
ccb22a2d28 | ||
|
fen
|
3d415edbdc | ||
|
poslop
|
7ca1b58362 | ||
|
poslop
|
8d0825ac09 | ||
|
poslop
|
4cb8a3e127 | ||
|
poslop
|
91dbf6f344 | ||
|
poslop
|
b600cdf51a | ||
|
poslop
|
47c9fa6386 | ||
|
poslop
|
b7d1119d6d | ||
|
poslop
|
44fe3c5772 | ||
|
poslop
|
556d0fa2e1 | ||
|
poslop
|
bdd5235f2e | ||
|
agent
|
94a4a3c2ec | ||
|
palette-agent
|
e08cafe9c8 | ||
|
Hermes Agent
|
2159982795 | ||
|
fen
|
bb5c4f0186 | ||
|
palette-agent
|
9811191648 | ||
|
poslop
|
5a2aa0f96d | ||
|
poslop
|
c288fc73a7 | ||
|
Hermes Agent
|
f6c4342468 | ||
|
poslop
|
f611cc3e9e | ||
|
poslop
|
594b5f01aa |
@@ -2,7 +2,7 @@ name: CI
|
||||
|
||||
on:
|
||||
push:
|
||||
branches: [main]
|
||||
branches: [main, dev]
|
||||
tags: ['v*']
|
||||
pull_request:
|
||||
|
||||
@@ -23,8 +23,8 @@ jobs:
|
||||
run: go test -v ./...
|
||||
|
||||
docker:
|
||||
# build & push image only on tags (releases)
|
||||
if: startsWith(github.ref, 'refs/tags/')
|
||||
# build & push image only on tags (releases) and dev branch (dev deploy)
|
||||
if: startsWith(github.ref, 'refs/tags/') || github.ref == 'refs/heads/dev'
|
||||
needs: test
|
||||
runs-on: [debian-latest]
|
||||
env:
|
||||
@@ -55,8 +55,9 @@ jobs:
|
||||
with:
|
||||
context: .
|
||||
push: true
|
||||
build-args: VERSION=${{ gitea.ref_name }}
|
||||
tags: |
|
||||
git.archfox.org/poslop/palette:${{ gitea.ref_name }}
|
||||
git.archfox.org/poslop/palette:latest
|
||||
${{ startsWith(gitea.ref, 'refs/tags/') && 'git.archfox.org/poslop/palette:latest' || '' }}
|
||||
cache-from: type=gha
|
||||
cache-to: type=gha,mode=max
|
||||
|
||||
@@ -9,7 +9,8 @@ COPY go.mod go.sum ./
|
||||
RUN go mod download
|
||||
|
||||
COPY . .
|
||||
RUN CGO_ENABLED=0 GOOS=linux go build -ldflags="-s -w" -o /palette ./cmd/palette
|
||||
ARG VERSION=dev
|
||||
RUN CGO_ENABLED=0 GOOS=linux go build -ldflags="-s -w -X palette/internal/web.Version=${VERSION}" -o /palette ./cmd/palette
|
||||
|
||||
# ---- runtime stage ----
|
||||
FROM alpine:3.20
|
||||
|
||||
@@ -0,0 +1,679 @@
|
||||
Palette - self-hosted pastebin with paste cans
|
||||
Copyright (C) 2026 poslop
|
||||
|
||||
This program is free software: you can redistribute it and/or modify
|
||||
it under the terms of the GNU Affero General Public License as
|
||||
published by the Free Software Foundation, version 3 of the License.
|
||||
|
||||
This program is distributed in the hope that it will be useful,
|
||||
but WITHOUT ANY WARRANTY; without even the implied warranty of
|
||||
MERCHANTABILITY or FITNESS FOR A PARTICULAR PURPOSE. See the
|
||||
GNU Affero General Public License for more details.
|
||||
|
||||
You should have received a copy of the GNU Affero General Public License
|
||||
along with this program. If not, see <https://www.gnu.org/licenses/>.
|
||||
|
||||
SPDX-License-Identifier: AGPL-3.0-only
|
||||
|
||||
--------------------------------------------------------------------------------
|
||||
GNU AFFERO GENERAL PUBLIC LICENSE
|
||||
Version 3, 19 November 2007
|
||||
|
||||
Copyright (C) 2007 Free Software Foundation, Inc. <https://fsf.org/>
|
||||
Everyone is permitted to copy and distribute verbatim copies
|
||||
of this license document, but changing it is not allowed.
|
||||
|
||||
Preamble
|
||||
|
||||
The GNU Affero General Public License is a free, copyleft license for
|
||||
software and other kinds of works, specifically designed to ensure
|
||||
cooperation with the community in the case of network server software.
|
||||
|
||||
The licenses for most software and other practical works are designed
|
||||
to take away your freedom to share and change the works. By contrast,
|
||||
our General Public Licenses are intended to guarantee your freedom to
|
||||
share and change all versions of a program--to make sure it remains free
|
||||
software for all its users.
|
||||
|
||||
When we speak of free software, we are referring to freedom, not
|
||||
price. Our General Public Licenses are designed to make sure that you
|
||||
have the freedom to distribute copies of free software (and charge for
|
||||
them if you wish), that you receive source code or can get it if you
|
||||
want it, that you can change the software or use pieces of it in new
|
||||
free programs, and that you know you can do these things.
|
||||
|
||||
Developers that use our General Public Licenses protect your rights
|
||||
with two steps: (1) assert copyright on the software, and (2) offer
|
||||
you this License which gives you legal permission to copy, distribute
|
||||
and/or modify the software.
|
||||
|
||||
A secondary benefit of defending all users' freedom is that
|
||||
improvements made in alternate versions of the program, if they
|
||||
receive widespread use, become available for other developers to
|
||||
incorporate. Many developers of free software are heartened and
|
||||
encouraged by the resulting cooperation. However, in the case of
|
||||
software used on network servers, this result may fail to come about.
|
||||
The GNU General Public License permits making a modified version and
|
||||
letting the public access it on a server without ever releasing its
|
||||
source code to the public.
|
||||
|
||||
The GNU Affero General Public License is designed specifically to
|
||||
ensure that, in such cases, the modified source code becomes available
|
||||
to the community. It requires the operator of a network server to
|
||||
provide the source code of the modified version running there to the
|
||||
users of that server. Therefore, public use of a modified version, on
|
||||
a publicly accessible server, gives the public access to the source
|
||||
code of the modified version.
|
||||
|
||||
An older license, called the Affero General Public License and
|
||||
published by Affero, was designed to accomplish similar goals. This is
|
||||
a different license, not a version of the Affero GPL, but Affero has
|
||||
released a new version of the Affero GPL which permits relicensing under
|
||||
this license.
|
||||
|
||||
The precise terms and conditions for copying, distribution and
|
||||
modification follow.
|
||||
|
||||
TERMS AND CONDITIONS
|
||||
|
||||
0. Definitions.
|
||||
|
||||
"This License" refers to version 3 of the GNU Affero General Public License.
|
||||
|
||||
"Copyright" also means copyright-like laws that apply to other kinds of
|
||||
works, such as semiconductor masks.
|
||||
|
||||
"The Program" refers to any copyrightable work licensed under this
|
||||
License. Each licensee is addressed as "you". "Licensees" and
|
||||
"recipients" may be individuals or organizations.
|
||||
|
||||
To "modify" a work means to copy from or adapt all or part of the work
|
||||
in a fashion requiring copyright permission, other than the making of an
|
||||
exact copy. The resulting work is called a "modified version" of the
|
||||
earlier work or a work "based on" the earlier work.
|
||||
|
||||
A "covered work" means either the unmodified Program or a work based
|
||||
on the Program.
|
||||
|
||||
To "propagate" a work means to do anything with it that, without
|
||||
permission, would make you directly or secondarily liable for
|
||||
infringement under applicable copyright law, except executing it on a
|
||||
computer or modifying a private copy. Propagation includes copying,
|
||||
distribution (with or without modification), making available to the
|
||||
public, and in some countries other activities as well.
|
||||
|
||||
To "convey" a work means any kind of propagation that enables other
|
||||
parties to make or receive copies. Mere interaction with a user through
|
||||
a computer network, with no transfer of a copy, is not conveying.
|
||||
|
||||
An interactive user interface displays "Appropriate Legal Notices"
|
||||
to the extent that it includes a convenient and prominently visible
|
||||
feature that (1) displays an appropriate copyright notice, and (2)
|
||||
tells the user that there is no warranty for the work (except to the
|
||||
extent that warranties are provided), that licensees may convey the
|
||||
work under this License, and how to view a copy of this License. If
|
||||
the interface presents a list of user commands or options, such as a
|
||||
menu, a prominent item in the list meets this criterion.
|
||||
|
||||
1. Source Code.
|
||||
|
||||
The "source code" for a work means the preferred form of the work
|
||||
for making modifications to it. "Object code" means any non-source
|
||||
form of a work.
|
||||
|
||||
A "Standard Interface" means an interface that either is an official
|
||||
standard defined by a recognized standards body, or, in the case of
|
||||
interfaces specified for a particular programming language, one that
|
||||
is widely used among developers working in that language.
|
||||
|
||||
The "System Libraries" of an executable work include anything, other
|
||||
than the work as a whole, that (a) is included in the normal form of
|
||||
packaging a Major Component, but which is not part of that Major
|
||||
Component, and (b) serves only to enable use of the work with that
|
||||
Major Component, or to implement a Standard Interface for which an
|
||||
implementation is available to the public in source code form. A
|
||||
"Major Component", in this context, means a major essential component
|
||||
(kernel, window system, and so on) of the specific operating system
|
||||
(if any) on which the executable work runs, or a compiler used to
|
||||
produce the work, or an object code interpreter used to run it.
|
||||
|
||||
The "Corresponding Source" for a work in object code form means all
|
||||
the source code needed to generate, install, and (for an executable
|
||||
work) run the object code and to modify the work, including scripts to
|
||||
control those activities. However, it does not include the work's
|
||||
System Libraries, or general-purpose tools or generally available free
|
||||
programs which are used unmodified in performing those activities but
|
||||
which are not part of the work. For example, Corresponding Source
|
||||
includes interface definition files associated with source files for
|
||||
the work, and the source code for shared libraries and dynamically
|
||||
linked subprograms that the work is specifically designed to require,
|
||||
such as by intimate data communication or control flow between those
|
||||
subprograms and other parts of the work.
|
||||
|
||||
The Corresponding Source need not include anything that users
|
||||
can regenerate automatically from other parts of the Corresponding
|
||||
Source.
|
||||
|
||||
The Corresponding Source for a work in source code form is that
|
||||
same work.
|
||||
|
||||
2. Basic Permissions.
|
||||
|
||||
All rights granted under this License are granted for the term of
|
||||
copyright on the Program, and are irrevocable provided the stated
|
||||
conditions are met. This License explicitly affirms your unlimited
|
||||
permission to run the unmodified Program. The output from running a
|
||||
covered work is covered by this License only if the output, given its
|
||||
content, constitutes a covered work. This License acknowledges your
|
||||
rights of fair use or other equivalent, as provided by copyright law.
|
||||
|
||||
You may make, run and propagate covered works that you do not
|
||||
convey, without conditions so long as your license otherwise remains
|
||||
in force. You may convey covered works to others for the sole purpose
|
||||
of having them make modifications exclusively for you, or provide you
|
||||
with facilities for running those works, provided that you comply with
|
||||
the terms of this License in conveying all material for which you do
|
||||
not control copyright. Those thus making or running the covered works
|
||||
for you must do so exclusively on your behalf, under your direction
|
||||
and control, on terms that prohibit them from making any copies of
|
||||
your copyrighted material outside their relationship with you.
|
||||
|
||||
Conveying under any other circumstances is permitted solely under
|
||||
the conditions stated below. Sublicensing is not allowed; section 10
|
||||
makes it unnecessary.
|
||||
|
||||
3. Protecting Users' Legal Rights From Anti-Circumvention Law.
|
||||
|
||||
No covered work shall be deemed part of an effective technological
|
||||
measure under any applicable law fulfilling obligations under article
|
||||
11 of the WIPO copyright treaty adopted on 20 December 1996, or
|
||||
similar laws prohibiting or restricting circumvention of such
|
||||
measures.
|
||||
|
||||
When you convey a covered work, you waive any legal power to forbid
|
||||
circumvention of technological measures to the extent such circumvention
|
||||
is effected by exercising rights under this License with respect to
|
||||
the covered work, and you disclaim any intention to limit operation or
|
||||
modification of the work as a means of enforcing, against the work's
|
||||
users, your or third parties' legal rights to forbid circumvention of
|
||||
technological measures.
|
||||
|
||||
4. Conveying Verbatim Copies.
|
||||
|
||||
You may convey verbatim copies of the Program's source code as you
|
||||
receive it, in any medium, provided that you conspicuously and
|
||||
appropriately publish on each copy an appropriate copyright notice;
|
||||
keep intact all notices stating that this License and any
|
||||
non-permissive terms added in accord with section 7 apply to the code;
|
||||
keep intact all notices of the absence of any warranty; and give all
|
||||
recipients a copy of this License along with the Program.
|
||||
|
||||
You may charge any price or no price for each copy that you convey,
|
||||
and you may offer support or warranty protection for a fee.
|
||||
|
||||
5. Conveying Modified Source Versions.
|
||||
|
||||
You may convey a work based on the Program, or the modifications to
|
||||
produce it from the Program, in the form of source code under the
|
||||
terms of section 4, provided that you also meet all of these conditions:
|
||||
|
||||
a) The work must carry prominent notices stating that you modified
|
||||
it, and giving a relevant date.
|
||||
|
||||
b) The work must carry prominent notices stating that it is
|
||||
released under this License and any conditions added under section
|
||||
7. This requirement modifies the requirement in section 4 to
|
||||
"keep intact all notices".
|
||||
|
||||
c) You must license the entire work, as a whole, under this
|
||||
License to anyone who comes into possession of a copy. This
|
||||
License will therefore apply, along with any applicable section 7
|
||||
additional terms, to the whole of the work, and all its parts,
|
||||
regardless of how they are packaged. This License gives no
|
||||
permission to license the work in any other way, but it does not
|
||||
invalidate such permission if you have separately received it.
|
||||
|
||||
d) If the work has interactive user interfaces, each must display
|
||||
Appropriate Legal Notices; however, if the Program has interactive
|
||||
interfaces that do not display Appropriate Legal Notices, your
|
||||
work need not make them do so.
|
||||
|
||||
A compilation of a covered work with other separate and independent
|
||||
works, which are not by their nature extensions of the covered work,
|
||||
and which are not combined with it such as to form a larger program,
|
||||
in or on a volume of a storage or distribution medium, is called an
|
||||
"aggregate" if the compilation and its resulting copyright are not
|
||||
used to limit the access or legal rights of the compilation's users
|
||||
beyond what the individual works permit. Inclusion of a covered work
|
||||
in an aggregate does not cause this License to apply to the other
|
||||
parts of the aggregate.
|
||||
|
||||
6. Conveying Non-Source Forms.
|
||||
|
||||
You may convey a covered work in object code form under the terms
|
||||
of sections 4 and 5, provided that you also convey the
|
||||
machine-readable Corresponding Source under the terms of this License,
|
||||
in one of these ways:
|
||||
|
||||
a) Convey the object code in, or embodied in, a physical product
|
||||
(including a physical distribution medium), accompanied by the
|
||||
Corresponding Source fixed on a durable physical medium
|
||||
customarily used for software interchange.
|
||||
|
||||
b) Convey the object code in, or embodied in, a physical product
|
||||
(including a physical distribution medium), accompanied by a
|
||||
written offer, valid for at least three years and valid for as
|
||||
long as you offer spare parts or customer support for that product
|
||||
model, to give anyone who possesses the object code either (1) a
|
||||
copy of the Corresponding Source for all the software in the
|
||||
product that is covered by this License, on a durable physical
|
||||
medium customarily used for software interchange, for a price no
|
||||
more than your reasonable cost of physically performing this
|
||||
conveying of source, or (2) access to copy the
|
||||
Corresponding Source from a network server at no charge.
|
||||
|
||||
c) Convey individual copies of the object code with a copy of the
|
||||
written offer to provide the Corresponding Source. This
|
||||
alternative is allowed only occasionally and noncommercially, and
|
||||
only if you received the object code with such an offer, in accord
|
||||
with subsection 6b.
|
||||
|
||||
d) Convey the object code by offering access from a designated
|
||||
place (gratis or for a charge), and offer equivalent access to the
|
||||
Corresponding Source in the same way through the same place at no
|
||||
further charge. You need not require recipients to copy the
|
||||
Corresponding Source along with the object code. If the place to
|
||||
copy the object code is a network server, the Corresponding Source
|
||||
may be on a different server (operated by you or a third party)
|
||||
that supports equivalent copying facilities, provided you maintain
|
||||
clear directions next to the object code saying where to find the
|
||||
Corresponding Source. Regardless of what server hosts the
|
||||
Corresponding Source, you remain obligated to ensure that it is
|
||||
available for as long as needed to satisfy these requirements.
|
||||
|
||||
e) Convey the object code using peer-to-peer transmission, provided
|
||||
you inform other peers where the object code and Corresponding
|
||||
Source of the work are being offered to the general public at no
|
||||
charge under subsection 6d.
|
||||
|
||||
A separable portion of the object code, whose source code is excluded
|
||||
from the Corresponding Source as a System Library, need not be
|
||||
included in conveying the object code work.
|
||||
|
||||
A "User Product" is either (1) a "consumer product", which means any
|
||||
tangible personal property which is normally used for personal, family,
|
||||
or household purposes, or (2) anything designed or sold for incorporation
|
||||
into a dwelling. In determining whether a product is a consumer product,
|
||||
doubtful cases shall be resolved in favor of coverage. For a particular
|
||||
product received by a particular user, "normally used" refers to a
|
||||
typical or common use of that class of product, regardless of the status
|
||||
of the particular user or of the way in which the particular user
|
||||
actually uses, or expects or is expected to use, the product. A product
|
||||
is a consumer product regardless of whether the product has substantial
|
||||
commercial, industrial or non-consumer uses, unless such uses represent
|
||||
the only significant mode of use of the product.
|
||||
|
||||
"Installation Information" for a User Product means any methods,
|
||||
procedures, authorization keys, or other information required to install
|
||||
and execute modified versions of a covered work in that User Product from
|
||||
a modified version of its Corresponding Source. The information must
|
||||
suffice to ensure that the continued functioning of the modified object
|
||||
code is in no case prevented or interfered with solely because
|
||||
modification has been made.
|
||||
|
||||
If you convey an object code work under this section in, or with, or
|
||||
specifically for use in, a User Product, and the conveying occurs as
|
||||
part of a transaction in which the right of possession and use of the
|
||||
User Product is transferred to the recipient in perpetuity or for a
|
||||
fixed term (regardless of how the transaction is characterized), the
|
||||
Corresponding Source conveyed under this section must be accompanied
|
||||
by the Installation Information. But this requirement does not apply
|
||||
if neither you nor any third party retains the ability to install
|
||||
modified object code on the User Product (for example, the work has
|
||||
been installed in ROM).
|
||||
|
||||
The requirement to provide Installation Information does not include a
|
||||
requirement to continue to provide support service, warranty, or updates
|
||||
for a work that has been modified or installed by the recipient, or for
|
||||
the User Product in which it has been modified or installed. Access to a
|
||||
network may be denied when the modification itself materially and
|
||||
adversely affects the operation of the network or violates the rules and
|
||||
protocols for communication across the network.
|
||||
|
||||
Corresponding Source conveyed, and Installation Information provided,
|
||||
in accord with this section must be in a format that is publicly
|
||||
documented (and with an implementation available to the public in
|
||||
source code form), and must require no special password or key for
|
||||
unpacking, reading or copying.
|
||||
|
||||
7. Additional Terms.
|
||||
|
||||
"Additional permissions" are terms that supplement the terms of this
|
||||
License by making exceptions from one or more of its conditions.
|
||||
Additional permissions that are applicable to the entire Program shall
|
||||
be treated as though they were included in this License, to the extent
|
||||
that they are valid under applicable law. If additional permissions
|
||||
apply only to part of the Program, that part may be used separately
|
||||
under those permissions, but the entire Program remains governed by
|
||||
this License without regard to the additional permissions.
|
||||
|
||||
When you convey a copy of a covered work, you may at your option
|
||||
remove any additional permissions from that copy, or from any part of
|
||||
it. (Additional permissions may be written to require their own
|
||||
removal in certain cases when you modify the work.) You may place
|
||||
additional permissions on material, added by you to a covered work,
|
||||
for which you have or can give appropriate copyright permission.
|
||||
|
||||
Notwithstanding any other provision of this License, for material you
|
||||
add to a covered work, you may (if authorized by the copyright holders of
|
||||
that material) supplement the terms of this License with terms:
|
||||
|
||||
a) Disclaiming warranty or limiting liability differently from the
|
||||
terms of sections 15 and 16 of this License; or
|
||||
|
||||
b) Requiring preservation of specified reasonable legal notices or
|
||||
author attributions in that material or in the Appropriate Legal
|
||||
Notices displayed by works containing it; or
|
||||
|
||||
c) Prohibiting misrepresentation of the origin of that material, or
|
||||
requiring that modified versions of such material be marked in
|
||||
reasonable ways as different from the original version; or
|
||||
|
||||
d) Limiting the use for publicity purposes of names of licensors or
|
||||
authors of the material; or
|
||||
|
||||
e) Declining to grant rights under trademark law for use of some
|
||||
trade names, trademarks, or service marks; or
|
||||
|
||||
f) Requiring indemnification of licensors and authors of that
|
||||
material by anyone who conveys the material (or modified versions of
|
||||
it) with contractual assumptions of liability to the recipient, for
|
||||
any liability that these contractual assumptions directly impose on
|
||||
those licensors and authors.
|
||||
|
||||
All other non-permissive additional terms are considered "further
|
||||
restrictions" within the meaning of section 10. If the Program as you
|
||||
received it, or any part of it, contains a notice stating that it is
|
||||
governed by this License along with a term that is a further
|
||||
restriction, you may remove that term. If a license document contains
|
||||
a further restriction but permits relicensing or conveying under this
|
||||
License, you may add to a covered work material governed by the terms
|
||||
of that license document, provided that the further restriction does
|
||||
not survive such relicensing or conveying.
|
||||
|
||||
If you add terms to a covered work in accord with this section, you
|
||||
must place, in the relevant source files, a statement of the
|
||||
additional terms that apply to those files, or a notice indicating
|
||||
where to find the applicable terms.
|
||||
|
||||
Additional terms, permissive or non-permissive, may be stated in the
|
||||
form of a separately written license, or stated as exceptions;
|
||||
the above requirements apply either way.
|
||||
|
||||
8. Termination.
|
||||
|
||||
You may not propagate or modify a covered work except as expressly
|
||||
provided under this License. Any attempt otherwise to propagate or
|
||||
modify it is void, and will automatically terminate your rights under
|
||||
this License (including any patent licenses granted under the third
|
||||
paragraph of section 11).
|
||||
|
||||
However, if you cease all violation of this License, then your
|
||||
license from a particular copyright holder is reinstated (a)
|
||||
provisionally, unless and until the copyright holder explicitly and
|
||||
finally terminates your license, and (b) permanently, if the copyright
|
||||
holder fails to notify you of the violation by some reasonable means
|
||||
prior to 60 days after the cessation.
|
||||
|
||||
Moreover, your license from a particular copyright holder is
|
||||
reinstated permanently if the copyright holder notifies you of the
|
||||
violation by some reasonable means, this is the first time you have
|
||||
received notice of violation of this License (for any work) from that
|
||||
copyright holder, and you cure the violation prior to 30 days after
|
||||
your receipt of the notice.
|
||||
|
||||
Termination of your rights under this section does not terminate the
|
||||
licenses of parties who have received copies or rights from you under
|
||||
this License. If your rights have been terminated and not permanently
|
||||
reinstated, you do not qualify to receive new licenses for the same
|
||||
material under section 10.
|
||||
|
||||
9. Acceptance Not Required for Having Copies.
|
||||
|
||||
You are not required to accept this License in order to receive or
|
||||
run a copy of the Program. Ancillary propagation of a covered work
|
||||
occurring solely as a consequence of using peer-to-peer transmission
|
||||
to receive a copy likewise does not require acceptance. However,
|
||||
nothing other than this License grants you permission to propagate or
|
||||
modify any covered work. These actions infringe copyright if you do
|
||||
not accept this License. Therefore, by modifying or propagating a
|
||||
covered work, you indicate your acceptance of this License to do so.
|
||||
|
||||
10. Automatic Licensing of Downstream Recipients.
|
||||
|
||||
Each time you convey a covered work, the recipient automatically
|
||||
receives a license from the original licensors, to run, modify and
|
||||
propagate that work, subject to this License. You are not responsible
|
||||
for enforcing compliance by third parties with this License.
|
||||
|
||||
An "entity transaction" is a transaction transferring control of an
|
||||
organization, or substantially all assets of one, or subdividing an
|
||||
organization, or merging organizations. If propagation of a covered
|
||||
work results from an entity transaction, each party to that
|
||||
transaction who receives a copy of the work also receives whatever
|
||||
licenses to the work the party's predecessor in interest had or could
|
||||
give under the previous paragraph, plus a right to possession of the
|
||||
Corresponding Source of the work from the predecessor in interest, if
|
||||
the predecessor has it or can get it with reasonable efforts.
|
||||
|
||||
You may not impose any further restrictions on the exercise of the
|
||||
rights granted or affirmed under this License. For example, you may
|
||||
not impose a license fee, royalty, or other charge for exercise of
|
||||
rights granted under this License, and you may not initiate litigation
|
||||
(including a cross-claim or counterclaim in a lawsuit) alleging that
|
||||
any patent claim is infringed by making, using, selling, offering for
|
||||
sale, or importing the Program or any portion of it.
|
||||
|
||||
11. Patents.
|
||||
|
||||
A "contributor" is a copyright holder who authorizes use under this
|
||||
License of the Program or a work on which the Program is based. The
|
||||
work thus licensed is called the contributor's "contributor version".
|
||||
|
||||
A contributor's "essential patent claims" are all patent claims
|
||||
owned or controlled by the contributor, whether already acquired or
|
||||
hereafter acquired, that would be infringed by some manner, permitted
|
||||
by this License, of making, using, or selling its contributor version,
|
||||
but do not include claims that would be infringed only as a
|
||||
consequence of further modification of the contributor version. For
|
||||
purposes of this definition, "control" includes the right to grant
|
||||
patent sublicenses in a manner consistent with the requirements of
|
||||
this License.
|
||||
|
||||
Each contributor grants you a non-exclusive, worldwide, royalty-free
|
||||
patent license under the contributor's essential patent claims, to
|
||||
make, use, sell, offer for sale, import and otherwise run, modify and
|
||||
propagate the contents of its contributor version.
|
||||
|
||||
In the following three paragraphs, a "patent license" is any express
|
||||
agreement or commitment, however denominated, not to enforce a patent
|
||||
(such as an express permission to practice a patent or covenant not to
|
||||
sue for patent infringement). To "grant" such a patent license to a
|
||||
party means to make such an agreement or commitment not to enforce a
|
||||
patent against the party.
|
||||
|
||||
If you convey a covered work, knowingly relying on a patent license,
|
||||
and the Corresponding Source of the work is not available for anyone
|
||||
to copy, free of charge and under the terms of this License, through a
|
||||
publicly available network server or other readily accessible means,
|
||||
then you must either (1) cause the Corresponding Source to be so
|
||||
available, or (2) arrange to deprive yourself of the benefit of the
|
||||
patent license for this particular work, or (3) arrange, in a manner
|
||||
consistent with the requirements of this License, to extend the patent
|
||||
license to downstream recipients. "Knowingly relying" means you have
|
||||
actual knowledge that, but for the patent license, your conveying the
|
||||
covered work in a country, or your recipient's use of the covered work
|
||||
in a country, would infringe one or more identifiable patents in that
|
||||
country that you have reason to believe are valid.
|
||||
|
||||
If, pursuant to or in connection with a single transaction or
|
||||
arrangement, you convey, or propagate by procuring conveyance of, a
|
||||
covered work, and grant a patent license to some of the parties
|
||||
receiving the covered work authorizing them to use, propagate, modify
|
||||
or convey a specific copy of the covered work, then the patent license
|
||||
you grant is automatically extended to all recipients of the covered
|
||||
work and works based on it.
|
||||
|
||||
A patent license is "discriminatory" if it does not include within
|
||||
the scope of its coverage, prohibits the exercise of, or is
|
||||
conditioned on the non-exercise of one or more of the rights that are
|
||||
specifically granted under this License. You may not convey a covered
|
||||
work if you are a party to an arrangement with a third party that is
|
||||
in the business of distributing software, under which you make payment
|
||||
to the third party based on the extent of your activity of conveying
|
||||
the work, and under which the third party grants, to any of the
|
||||
parties who would receive the covered work from you, a discriminatory
|
||||
patent license (a) in connection with copies of the covered work
|
||||
conveyed by you (or copies made from those copies), or (b) primarily
|
||||
for and in connection with specific products or compilations that
|
||||
contain the covered work, unless you entered into that arrangement,
|
||||
or that patent license was granted, prior to 28 March 2007.
|
||||
|
||||
Nothing in this License shall be construed as excluding or limiting
|
||||
any implied license or other defenses to infringement that may
|
||||
otherwise be available to you under applicable patent law.
|
||||
|
||||
12. No Surrender of Others' Freedom.
|
||||
|
||||
If conditions are imposed on you (whether by court order, agreement or
|
||||
otherwise) that contradict the conditions of this License, they do not
|
||||
excuse you from the conditions of this License. If you cannot convey a
|
||||
covered work so as to satisfy simultaneously your obligations under this
|
||||
License and any other pertinent obligations, then as a consequence you may
|
||||
not convey it at all. For example, if you agree to terms that obligate you
|
||||
to collect a royalty for further conveying from those to whom you convey
|
||||
the Program, the only way you could satisfy both those terms and this
|
||||
License would be to refrain entirely from conveying the Program.
|
||||
|
||||
13. Remote Network Interaction; Use with the GNU General Public License.
|
||||
|
||||
Notwithstanding any other provision of this License, if you modify the
|
||||
Program, your modified version must prominently offer all users
|
||||
interacting with it remotely through a computer network (if your version
|
||||
supports such interaction) an opportunity to receive the Corresponding
|
||||
Source of your version by providing access to the Corresponding Source
|
||||
from a network server at no charge, through some standard or customary
|
||||
means of facilitating copying of software. This Corresponding Source
|
||||
shall include the Corresponding Source for any work covered by version 3
|
||||
of the GNU General Public License that is incorporated pursuant to the
|
||||
following paragraph.
|
||||
|
||||
Notwithstanding any other provision of this License, you have
|
||||
permission to link or combine any covered work with a work licensed
|
||||
under version 3 of the GNU General Public License into a single
|
||||
combined work, and to convey the resulting work. The terms of this
|
||||
License will continue to apply to the part which is the covered work,
|
||||
but the work with which it is combined will remain governed by version
|
||||
3 of the GNU General Public License.
|
||||
|
||||
14. Revised Versions of this License.
|
||||
|
||||
The Free Software Foundation may publish revised and/or new versions of
|
||||
the GNU Affero General Public License from time to time. Such new versions
|
||||
will be similar in spirit to the present version, but may differ in detail to
|
||||
address new problems or concerns.
|
||||
|
||||
Each version is given a distinguishing version number. If the
|
||||
Program specifies that a certain numbered version of the GNU Affero General
|
||||
Public License "or any later version" applies to it, you have the
|
||||
option of following the terms and conditions either of that numbered
|
||||
version or of any later version published by the Free Software
|
||||
Foundation. If the Program does not specify a version number of the
|
||||
GNU Affero General Public License, you may choose any version ever published
|
||||
by the Free Software Foundation.
|
||||
|
||||
If the Program specifies that a proxy can decide which future
|
||||
versions of the GNU Affero General Public License can be used, that proxy's
|
||||
public statement of acceptance of a version permanently authorizes you
|
||||
to choose that version for the Program.
|
||||
|
||||
Later license versions may give you additional or different
|
||||
permissions. However, no additional obligations are imposed on any
|
||||
author or copyright holder as a result of your choosing to follow a
|
||||
later version.
|
||||
|
||||
15. Disclaimer of Warranty.
|
||||
|
||||
THERE IS NO WARRANTY FOR THE PROGRAM, TO THE EXTENT PERMITTED BY
|
||||
APPLICABLE LAW. EXCEPT WHEN OTHERWISE STATED IN WRITING THE COPYRIGHT
|
||||
HOLDERS AND/OR OTHER PARTIES PROVIDE THE PROGRAM "AS IS" WITHOUT WARRANTY
|
||||
OF ANY KIND, EITHER EXPRESSED OR IMPLIED, INCLUDING, BUT NOT LIMITED TO,
|
||||
THE IMPLIED WARRANTIES OF MERCHANTABILITY AND FITNESS FOR A PARTICULAR
|
||||
PURPOSE. THE ENTIRE RISK AS TO THE QUALITY AND PERFORMANCE OF THE PROGRAM
|
||||
IS WITH YOU. SHOULD THE PROGRAM PROVE DEFECTIVE, YOU ASSUME THE COST OF
|
||||
ALL NECESSARY SERVICING, REPAIR OR CORRECTION.
|
||||
|
||||
16. Limitation of Liability.
|
||||
|
||||
IN NO EVENT UNLESS REQUIRED BY APPLICABLE LAW OR AGREED TO IN WRITING
|
||||
WILL ANY COPYRIGHT HOLDER, OR ANY OTHER PARTY WHO MODIFIES AND/OR CONVEYS
|
||||
THE PROGRAM AS PERMITTED ABOVE, BE LIABLE TO YOU FOR DAMAGES, INCLUDING ANY
|
||||
GENERAL, SPECIAL, INCIDENTAL OR CONSEQUENTIAL DAMAGES ARISING OUT OF THE
|
||||
USE OR INABILITY TO USE THE PROGRAM (INCLUDING BUT NOT LIMITED TO LOSS OF
|
||||
DATA OR DATA BEING RENDERED INACCURATE OR LOSSES SUSTAINED BY YOU OR THIRD
|
||||
PARTIES OR A FAILURE OF THE PROGRAM TO OPERATE WITH ANY OTHER PROGRAMS),
|
||||
EVEN IF SUCH HOLDER OR OTHER PARTY HAS BEEN ADVISED OF THE POSSIBILITY OF
|
||||
SUCH DAMAGES.
|
||||
|
||||
17. Interpretation of Sections 15 and 16.
|
||||
|
||||
If the disclaimer of warranty and limitation of liability provided
|
||||
above cannot be given local legal effect according to their terms,
|
||||
reviewing courts shall apply local law that most closely approximates
|
||||
an absolute waiver of all civil liability in connection with the
|
||||
Program, unless a warranty or assumption of liability accompanies a
|
||||
copy of the Program in return for a fee.
|
||||
|
||||
END OF TERMS AND CONDITIONS
|
||||
|
||||
How to Apply These Terms to Your New Programs
|
||||
|
||||
If you develop a new program, and you want it to be of the greatest
|
||||
possible use to the public, the best way to achieve this is to make it
|
||||
free software which everyone can redistribute and change under these terms.
|
||||
|
||||
To do so, attach the following notices to the program. It is safest
|
||||
to attach them to the start of each source file to most effectively
|
||||
state the exclusion of warranty; and each file should have at least
|
||||
the "copyright" line and a pointer to where the full notice is found.
|
||||
|
||||
<one line to give the program's name and a brief idea of what it does.>
|
||||
Copyright (C) <year> <name of author>
|
||||
|
||||
This program is free software: you can redistribute it and/or modify
|
||||
it under the terms of the GNU Affero General Public License as published by
|
||||
the Free Software Foundation, either version 3 of the License, or
|
||||
(at your option) any later version.
|
||||
|
||||
This program is distributed in the hope that it will be useful,
|
||||
but WITHOUT ANY WARRANTY; without even the implied warranty of
|
||||
MERCHANTABILITY or FITNESS FOR A PARTICULAR PURPOSE. See the
|
||||
GNU Affero General Public License for more details.
|
||||
|
||||
You should have received a copy of the GNU Affero General Public License
|
||||
along with this program. If not, see <https://www.gnu.org/licenses/>.
|
||||
|
||||
Also add information on how to contact you by electronic and paper mail.
|
||||
|
||||
If your software can interact with users remotely through a computer
|
||||
network, you should also make sure that it provides a way for users to
|
||||
get its source. For example, if your program is a web application, its
|
||||
interface could display a "Source" link that leads users to an archive
|
||||
of the code. There are many ways you could offer source, and different
|
||||
solutions will be better for different programs; see section 13 for the
|
||||
specific requirements.
|
||||
|
||||
You should also get your employer (if you work as a programmer) or school,
|
||||
if any, to sign a "copyright disclaimer" for the program, if necessary.
|
||||
For more information on this, and how to apply and follow the GNU AGPL, see
|
||||
<https://www.gnu.org/licenses/>.
|
||||
@@ -1,33 +1,34 @@
|
||||
# Palette
|
||||
|
||||
Palette is a fast, self-hosted pastebin. One Go binary, a SQLite database, and
|
||||
a web UI for sharing code and text with links that expire on your terms.
|
||||
a web UI for sharing text and small files
|
||||
|
||||
> [!NOTE]
|
||||
> <table><tr><td>
|
||||
> <sub>✨ This project was built by AI — <strong>GLM 5.3 Flash</strong> on the <strong>Hermes Agent</strong> harness, with a human in the loop.</sub>
|
||||
> </td></tr></table>
|
||||
|
||||
## Features
|
||||
|
||||
- Paste cans — bundle notes, text, and files into one shareable page, with password/expiry/custom-slug parity and a `can` badge in listings
|
||||
- Password lock — protect individual pastes with a password
|
||||
- Custom expiry — from 1 minute up to 1 year, or never
|
||||
- Burn after N reads — a paste that vanishes after a chosen number of reads
|
||||
- Custom URLs — reserve `/my-snippet` instead of a random slug
|
||||
- Multiple files in one paste
|
||||
- Password protected pastes
|
||||
- Expir after a specified time
|
||||
- Burn after a number of views
|
||||
- Custom URLs
|
||||
- Syntax highlighting with language auto-detection (go-enry)
|
||||
- Rate limiting on create and unlock
|
||||
- Saved page — see and manage everything created from your browser
|
||||
- API-first — every UI action is also a plain HTTP call
|
||||
- Single binary — templates and assets are embedded; no external deps
|
||||
- Local cookie based submission history
|
||||
- Cookie based settings
|
||||
- Themes!
|
||||
|
||||
## Screenshots
|
||||
|
||||
| | |
|
||||
|---|---|
|
||||
| 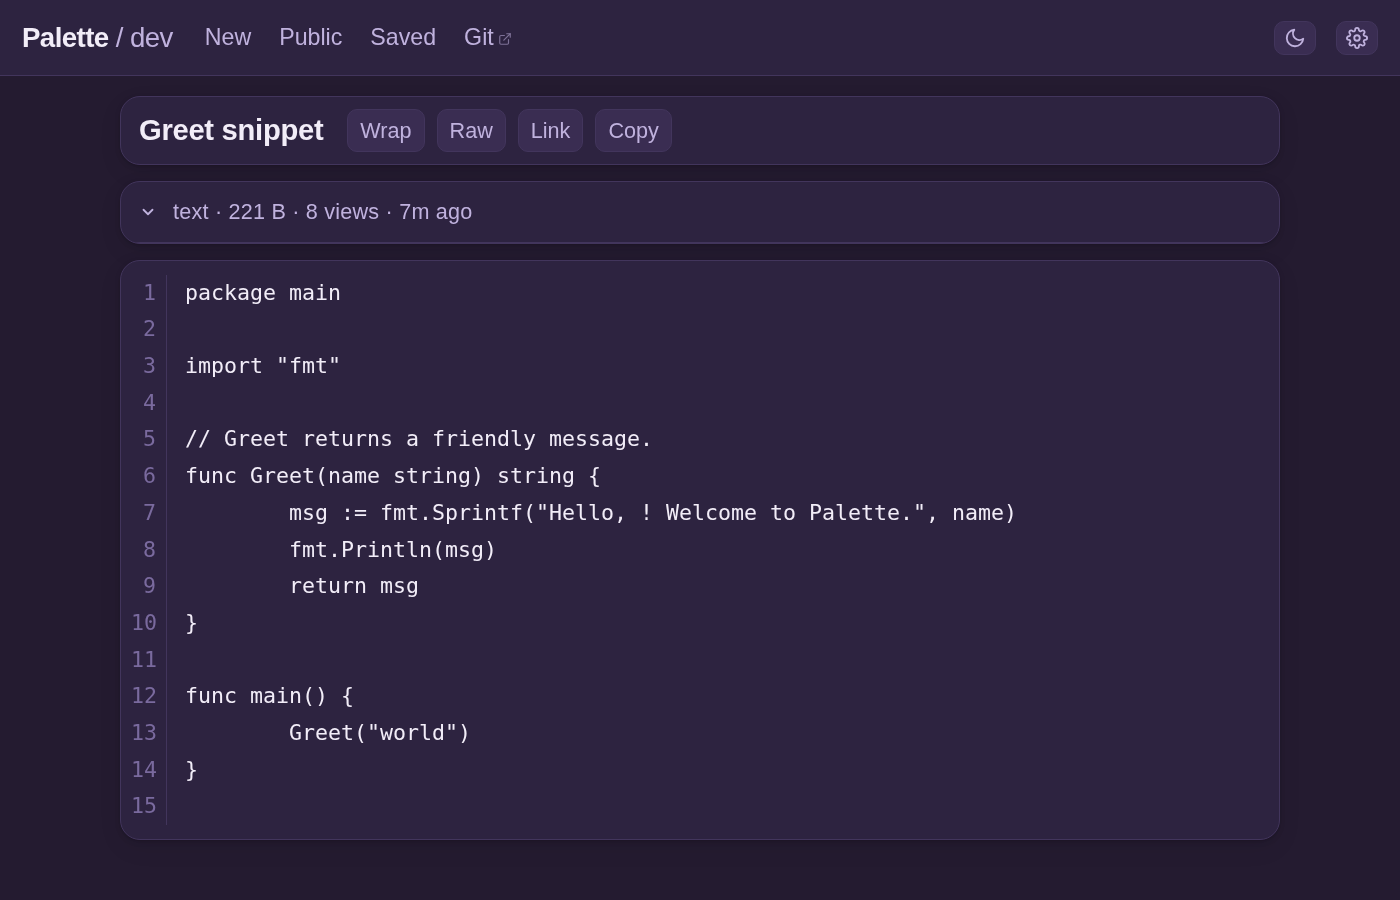 | 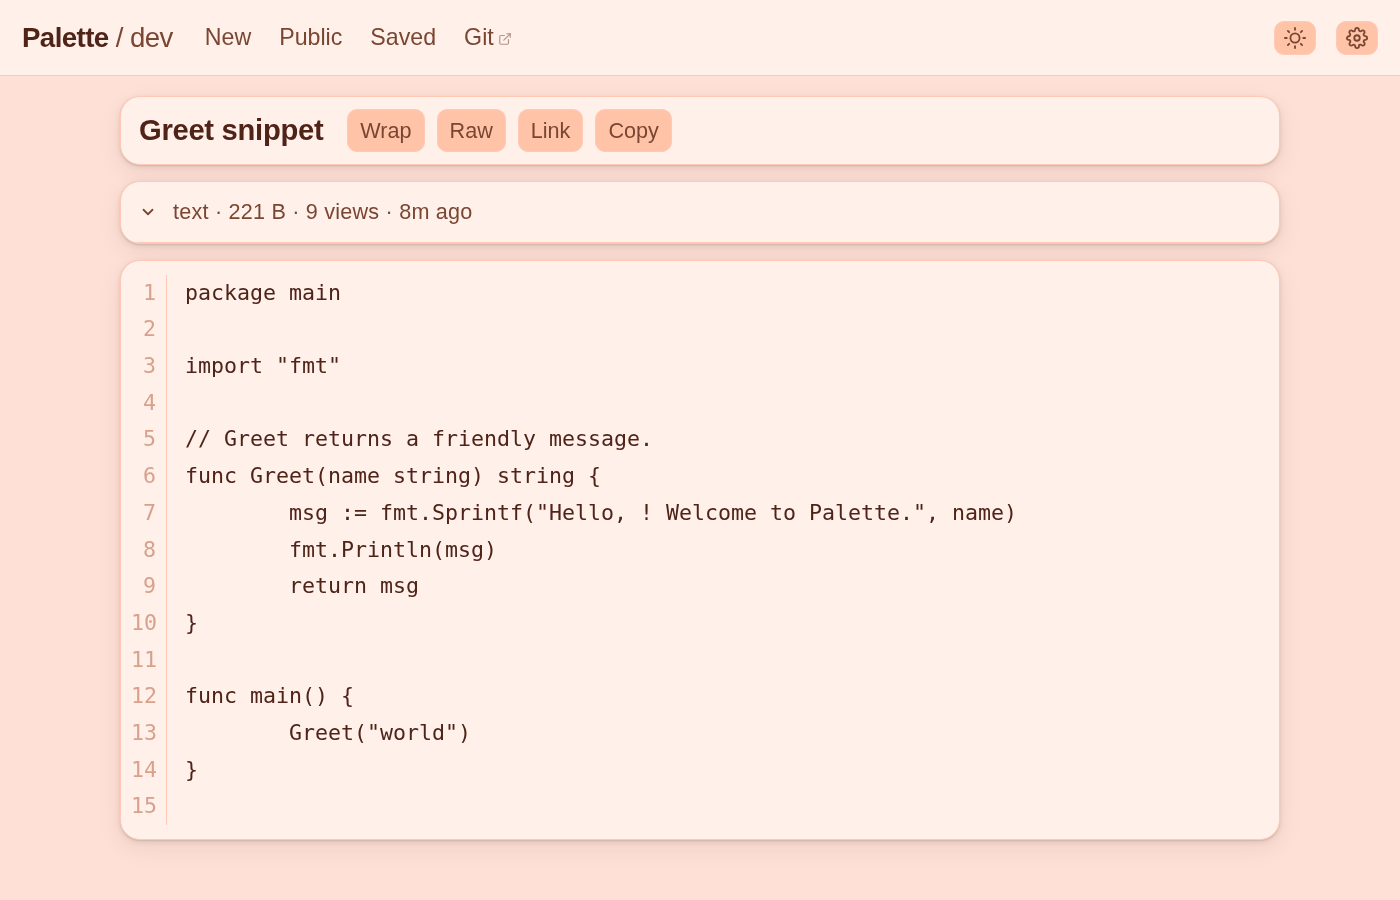 |
|
||||
| 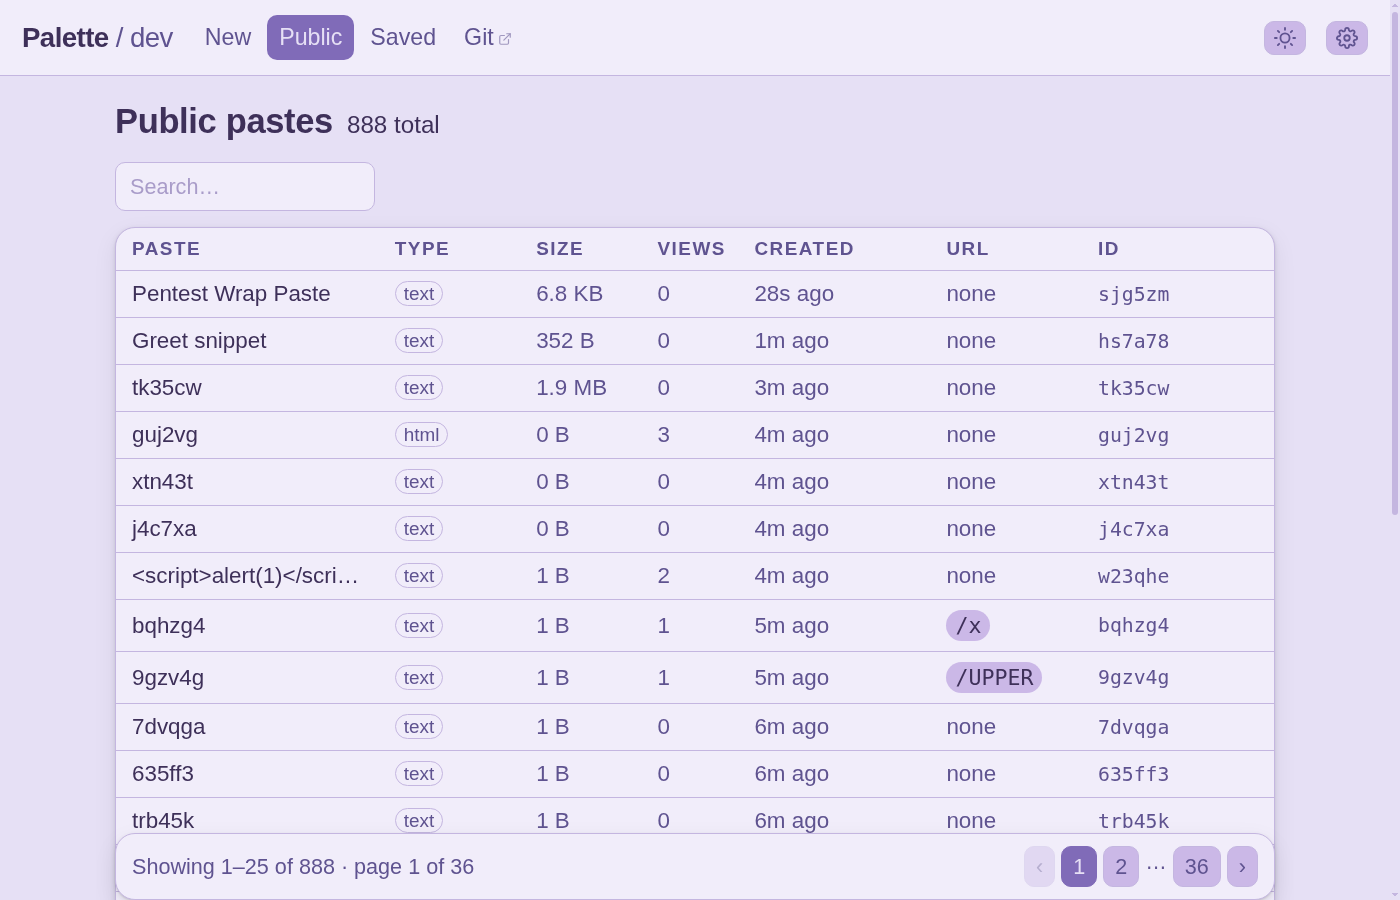 | 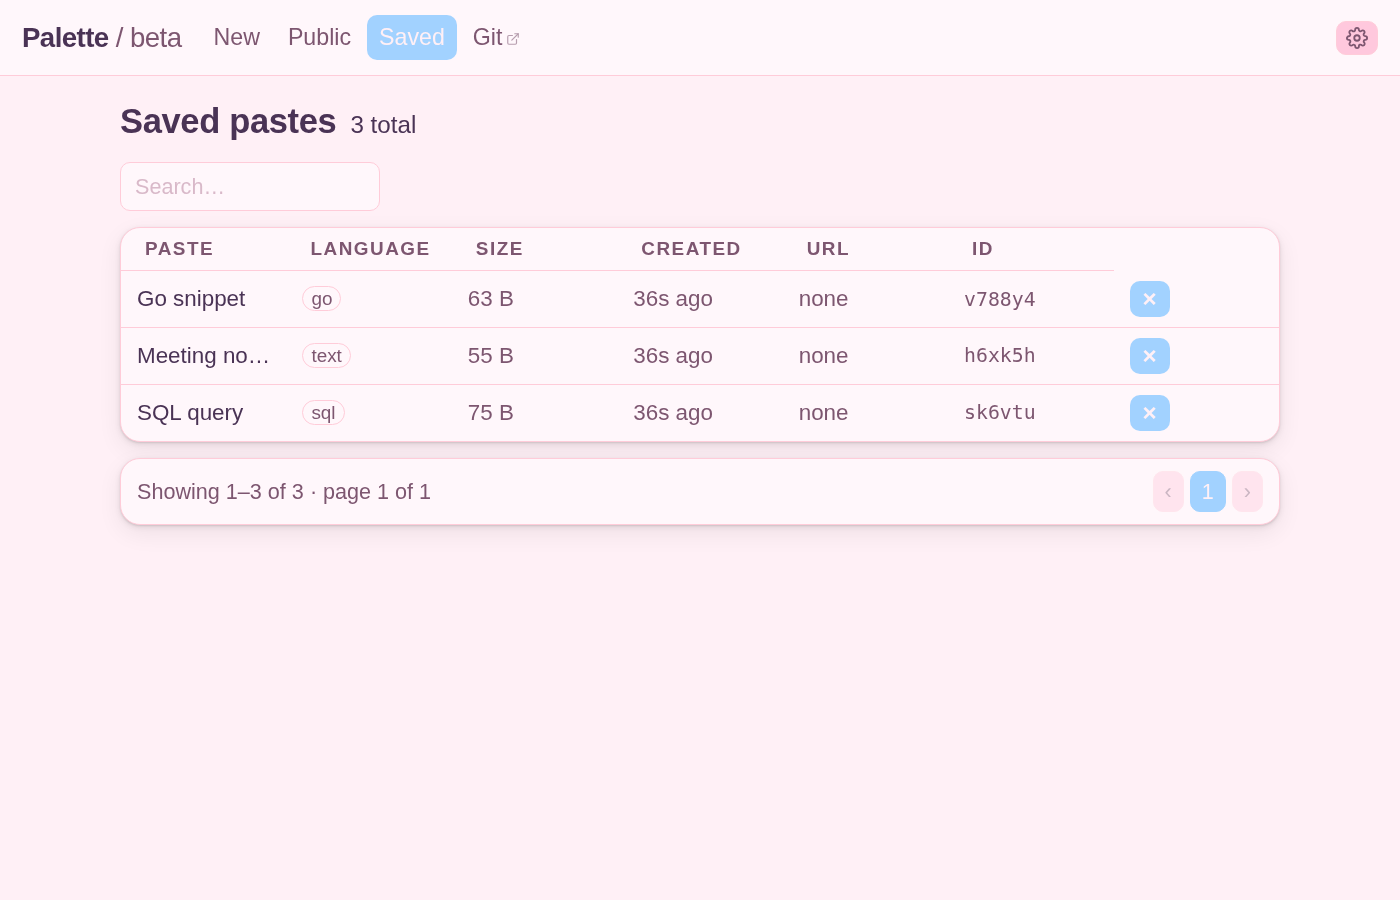 |
|
||||
|
||||
## Get Started
|
||||
|
||||
### Build from source
|
||||
|
||||
Requires Go 1.21+.
|
||||
|
||||
```bash
|
||||
go build -o palette .
|
||||
./palette
|
||||
# open http://localhost:8080
|
||||
```
|
||||
|
||||
### Docker
|
||||
|
||||
```bash
|
||||
@@ -36,12 +37,22 @@ docker run -p 8080:8080 -v palette-data:/data git.archfox.org/poslop/palette
|
||||
|
||||
The SQLite database lives in the `/data` volume inside the container.
|
||||
|
||||
## Screenshots
|
||||
## Docker Compose
|
||||
|
||||
See [docker-compose.yml](docker-compose.yml) for a ready-to-use example with
|
||||
every environment variable documented, including which are required (only the
|
||||
/data volume) and which are optional.
|
||||
|
||||
### Build from source
|
||||
|
||||
Requires Go 1.27+.
|
||||
|
||||
```bash
|
||||
go build -o palette ./cmd/palette
|
||||
./palette
|
||||
# open http://localhost:8080
|
||||
```
|
||||
|
||||
| | |
|
||||
|---|---|
|
||||
|  |  |
|
||||
|  | |
|
||||
|
||||
## Configuration
|
||||
|
||||
@@ -53,34 +64,34 @@ The SQLite database lives in the `/data` volume inside the container.
|
||||
| `PALETTE_MAX_ITEM` | `26214400` | Max can item size in bytes (25 MB) |
|
||||
| `PALETTE_ADMIN_KEY` | generated | Admin key; if unset a 32-char hex key is generated and persisted to `<db-dir>/admin-key` (0600) |
|
||||
|
||||
### Admin
|
||||
|
||||
`GET /admin` serves the admin page. Enter the admin key there — it is stored in
|
||||
`sessionStorage` (never a cookie) and sent as the `X-Admin-Key` header on
|
||||
`GET`/`POST /admin/api/settings`.
|
||||
|
||||
The admin API reads/sets: rate-limit burst, rate-limit refill per minute, max
|
||||
content bytes, default expiry, custom URL reservation days, and the burn
|
||||
viewer window (minutes). All admin access attempts are logged.
|
||||
|
||||
```bash
|
||||
./palette --reset-admin-key # regenerate the admin key and print it
|
||||
```
|
||||
An `/admin` page exists for runtime settings, protected by a key set at
|
||||
install (`PALETTE_ADMIN_KEY` env var) and resettable locally — see
|
||||
[API](https://git.archfox.org/poslop/palette/wiki/API) and the [design docs](https://git.archfox.org/poslop/palette/wiki/Home) in the wiki for details.
|
||||
|
||||
## API
|
||||
|
||||
Create a paste with one call:
|
||||
Full REST API: [wiki/API](https://git.archfox.org/poslop/palette/wiki/API). One example:
|
||||
|
||||
```bash
|
||||
curl -X POST http://localhost:8080/api/pastes \
|
||||
-H "Content-Type: application/json" \
|
||||
-d '{"content": "print(hello)", "language": "python", "expires_in": "168h"}'
|
||||
curl -X POST http://localhost:8080/api/pastes -d '{"content":"hello"}'
|
||||
```
|
||||
|
||||
Full API docs: [docs/API.md](docs/API.md).
|
||||
Design docs: [wiki/design](https://git.archfox.org/poslop/palette/wiki/design-attachments-storage) (e2e encryption, attachments & storage, cookie preferences).
|
||||
|
||||
## CI
|
||||
|
||||
Gitea Actions workflow at `.gitea/workflows/ci.yml`:
|
||||
- On push to main: `go vet` + `go test`
|
||||
- On tags: build and push Docker image to `git.archfox.org/poslop/palette`
|
||||
|
||||
|
||||
## License
|
||||
|
||||
Palette is licensed under the GNU Affero General Public License v3.0
|
||||
(AGPL-3.0-only). See [LICENSE](LICENSE).
|
||||
|
||||
The software is provided AS IS, without warranty of any kind, express or
|
||||
implied, including merchantability and fitness for a particular purpose.
|
||||
In no event shall the authors be liable for any claim, damages, or other
|
||||
liability, including without limitation any security vulnerabilities,
|
||||
data loss, or legal issues arising from use of the software. You use it
|
||||
at your own risk.
|
||||
|
||||
If you run a modified version of Palette as a network service, the AGPL
|
||||
requires you to offer your modified source code to its users.
|
||||
|
||||
@@ -0,0 +1,46 @@
|
||||
# Example docker-compose deployment for Palette.
|
||||
# All environment variables are optional; sensible defaults apply.
|
||||
# The only hard requirement is a volume on /data so the SQLite database
|
||||
# and the auto-generated admin key survive restarts.
|
||||
|
||||
services:
|
||||
palette:
|
||||
image: git.archfox.org/poslop/palette:v0.2.2
|
||||
# image: git.archfox.org/poslop/palette:latest # tracks main, less stable
|
||||
restart: unless-stopped
|
||||
ports:
|
||||
- "8080:8080" # host:container; the app listens on :8080
|
||||
volumes:
|
||||
- palette-data:/data # REQUIRED: SQLite db, admin key, attachments
|
||||
environment:
|
||||
# Address the server binds to inside the container.
|
||||
# Default: ":8080". Only change if you also change the ports mapping.
|
||||
PALETTE_ADDR: ":8080"
|
||||
|
||||
# Path to the SQLite database file.
|
||||
# Default: "/data/palette.db". Keep it on the /data volume.
|
||||
PALETTE_DB: "/data/palette.db"
|
||||
|
||||
# Admin API key for /admin/api/settings (rate limits, size caps, expiry).
|
||||
# Default: random key generated on first start and persisted to
|
||||
# /data/admin-key (mode 0600). Read it with:
|
||||
# docker compose exec palette cat /data/admin-key
|
||||
# Set this only if you want a fixed key (e.g. for automation).
|
||||
# PALETTE_ADMIN_KEY: "change-me"
|
||||
|
||||
# Max size in bytes of a single text paste. Oversized creates get 413.
|
||||
# Default: 5242880 (5 MiB).
|
||||
# PALETTE_MAX_TEXT: "5242880"
|
||||
|
||||
# Max size in bytes of a single can item (file/text inside a can).
|
||||
# Default: 26214400 (25 MiB).
|
||||
# PALETTE_MAX_ITEM: "26214400"
|
||||
|
||||
# HMAC secret for password-unlock cookies. Default: random per start,
|
||||
# which logs out every unlocked browser session on restart. Set a fixed
|
||||
# secret (any random string) to keep unlock sessions across restarts,
|
||||
# or when running multiple replicas that must agree.
|
||||
# PALETTE_UNLOCK_SECRET: "generate-with-openssl-rand-base64-32"
|
||||
|
||||
volumes:
|
||||
palette-data:
|
||||
@@ -1,120 +0,0 @@
|
||||
# Palette API
|
||||
|
||||
All endpoints are JSON unless noted. The web UI is served from the same port.
|
||||
|
||||
## Create paste
|
||||
|
||||
```bash
|
||||
curl -X POST http://localhost:8080/api/pastes \
|
||||
-H "Content-Type: application/json" \
|
||||
-d '{
|
||||
"content": "print(hello)",
|
||||
"title": "my snippet",
|
||||
"language": "python",
|
||||
"expires_in": "168h",
|
||||
"password": "optional",
|
||||
"custom_slug": "optional",
|
||||
"burn_after_read": false,
|
||||
"burn_after_reads": 1,
|
||||
"visibility": "public"
|
||||
}'
|
||||
```
|
||||
|
||||
- `expires_in` is a Go duration string (`90m`, `6h`, `336h`). Omit for no expiry.
|
||||
- `visibility` is `public` or `unlisted`.
|
||||
- `burn_after_reads` sets how many reads the paste survives (default 1 when
|
||||
`burn_after_read` is true). A read is counted per unique viewer session;
|
||||
the same viewer returning within 15 minutes does not count again.
|
||||
- Response includes `id`, `url`, `raw_url`, `api_url`, `expires_at`,
|
||||
`created_at`, and a one-time `deletion_token`.
|
||||
|
||||
Errors: `400` invalid body/content too large/duplicate slug, `401` password
|
||||
required, `404` paste expired/burned/gone, `413` content exceeds max bytes,
|
||||
`429` rate limited.
|
||||
|
||||
## Get paste
|
||||
|
||||
```bash
|
||||
curl http://localhost:8080/api/pastes/{id}
|
||||
# password-protected pastes:
|
||||
curl "http://localhost:8080/api/pastes/{id}?password=secret"
|
||||
# or via header: X-Paste-Password: secret
|
||||
```
|
||||
|
||||
The response includes `reads_remaining` (`null` when no read budget is set).
|
||||
|
||||
## Raw content
|
||||
|
||||
```bash
|
||||
curl http://localhost:8080/raw/{id}
|
||||
```
|
||||
|
||||
Raw reads count against a burn-after-read budget, same as page views.
|
||||
|
||||
## Delete
|
||||
|
||||
```bash
|
||||
# soft delete (requires the deletion token from the create response)
|
||||
curl -X DELETE -H "Authorization: Bearer TOKEN" http://localhost:8080/api/pastes/{id}
|
||||
# ...or via query param; the creator browser (viewer cookie) may also delete without a token
|
||||
curl -X DELETE "http://localhost:8080/api/pastes/{id}?token=TOKEN"
|
||||
|
||||
# hard delete immediately (requires the one-time deletion token)
|
||||
curl -X DELETE "http://localhost:8080/api/pastes/{id}/redeem?token=TOKEN"
|
||||
```
|
||||
|
||||
## Lists
|
||||
|
||||
```bash
|
||||
curl "http://localhost:8080/api/public?limit=25&offset=0" # public history
|
||||
curl http://localhost:8080/api/mine # this browser's pastes (viewer cookie)
|
||||
```
|
||||
|
||||
## Language detection
|
||||
|
||||
```bash
|
||||
curl -X POST http://localhost:8080/api/guess-language \
|
||||
-H "Content-Type: application/json" \
|
||||
-d '{"content": "package main"}'
|
||||
```
|
||||
|
||||
## Cans (bundles of items)
|
||||
|
||||
A can bundles multiple text items (and files) into one shareable page at
|
||||
`/can/{id}`. Password, expiry, visibility, custom slug, and viewer-scoped
|
||||
deletion work exactly like pastes; cans appear as normal rows (with a `can`
|
||||
badge) in `/api/public` and `/api/mine`.
|
||||
|
||||
```bash
|
||||
curl -X POST http://localhost:8080/api/pastes/can \
|
||||
-F "title=My bundle" \
|
||||
-F "expires_in=48h" \
|
||||
-F "custom_slug=my-bundle" \
|
||||
-F 'json_items=[{"title":"notes.txt","content":"some notes"}]' \
|
||||
-F "files=@screenshot.png" \
|
||||
-F "files=@log.txt"
|
||||
|
||||
curl http://localhost:8080/api/cans/{id}
|
||||
curl http://localhost:8080/api/cans/{id}/items/{item_id}
|
||||
curl -X DELETE http://localhost:8080/api/cans/{id} # creator browser only (vwr cookie)
|
||||
```
|
||||
|
||||
Password-protected cans use the same unlock flow as pastes: `POST /can/{id}`
|
||||
with the password sets an HMAC-bound cookie; item fetches accept the cookie as
|
||||
well as the `X-Paste-Password` header / `?password=` query param.
|
||||
|
||||
## Web pages
|
||||
|
||||
- `/new` — create a paste
|
||||
- `/history` — public paste history
|
||||
- `/mine` — pastes created from this browser
|
||||
- `/{id}` — view a paste
|
||||
- `/unlock/{id}` — password gate for protected pastes
|
||||
- `/raw/{id}` — raw content with original content type
|
||||
|
||||
## Expiry and deletion
|
||||
|
||||
- Expired pastes are soft-deleted by a background sweeper (runs every minute).
|
||||
- Soft-deleted pastes are hard-deleted after a 7-day grace period.
|
||||
- Deletion tokens allow immediate hard delete.
|
||||
- Burn-after-read pastes are soft-deleted once the read budget is exhausted.
|
||||

|
Before Width: | Height: | Size: 110 KiB |

|
Before Width: | Height: | Size: 68 KiB |

|
Before Width: | Height: | Size: 40 KiB |

|
Before Width: | Height: | Size: 109 KiB |

|
Before Width: | Height: | Size: 68 KiB |

|
Before Width: | Height: | Size: 41 KiB |

|
Before Width: | Height: | Size: 111 KiB |

|
Before Width: | Height: | Size: 70 KiB |

|
Before Width: | Height: | Size: 42 KiB |

|
Before Width: | Height: | Size: 111 KiB |

|
Before Width: | Height: | Size: 69 KiB |

|
Before Width: | Height: | Size: 42 KiB |

|
Before Width: | Height: | Size: 108 KiB |

|
Before Width: | Height: | Size: 67 KiB |

|
Before Width: | Height: | Size: 40 KiB |
@@ -1,60 +0,0 @@
|
||||
# Performance notes (#32)
|
||||
|
||||
Background: history and saved pages filter client-side. Each load fetches the
|
||||
most recent rows from the list endpoint (`limit=500` per query is the current
|
||||
client cap in `static/table.js`) and filters/sorts in the browser. This note
|
||||
records current behavior, measured latency, and the design for a future
|
||||
server-side search endpoint. Measurements only — no implementation in #4/#32.
|
||||
|
||||
## Current behavior
|
||||
|
||||
- `/api/public?limit=500&offset=0` and `/api/mine?limit=500&offset=0` return up
|
||||
to 500 rows (id, title, language, created_at, view_count, size,
|
||||
custom_slug, is_can). Content is NOT included — only `LENGTH(content)`.
|
||||
- The browser applies the search-box filter (title/language/id substring) and
|
||||
column sorting locally over the fetched window.
|
||||
- Consequence: search only covers the fetched window (500 most recent rows).
|
||||
Older rows are invisible to search until paginated through, and each query
|
||||
ships ~4 KB of row metadata regardless of how few rows the user will look at.
|
||||
|
||||
## Measured latency (synthetic rows, scratch SQLite DB)
|
||||
|
||||
Rows are synthetic pastes (~200 B content each, indexed like production:
|
||||
`idx_pastes_visibility_created`). Queried `GET /api/public?limit=500`
|
||||
(modernc.org/sqlite, WAL, single connection — same as production).
|
||||
|
||||
| Rows in table | Bulk insert | First query | Avg query (10 runs) | Payload |
|
||||
|---|---|---|---|---|
|
||||
| 1,000 | 19 ms | 1.0 ms | 0.44 ms | ~4.1 KB |
|
||||
| 5,000 | 95 ms | 1.0 ms | 0.98 ms | ~4.1 KB |
|
||||
| 10,000 | 189 ms | 2.0 ms | 1.78 ms | ~4.1 KB |
|
||||
|
||||
Interpretation:
|
||||
|
||||
- The list query itself is cheap (< 2 ms at 10k rows); latency users perceive
|
||||
comes from network + browser rendering of 500 rows, not SQL.
|
||||
- The current design scales fine to ~10k pastes. Beyond that, shipping 500
|
||||
rows per keystroke-refresh cycle is wasteful and search coverage stays
|
||||
capped at the window.
|
||||
|
||||
## Future design: server-side `/api/search?q=` (#32 remainder)
|
||||
|
||||
- Endpoint: `GET /api/search?q=<term>&limit=25&offset=0`.
|
||||
- SQL: `SELECT ... FROM pastes WHERE deleted_at IS NULL AND (expires_at IS NULL
|
||||
OR expires_at > ?) AND (title LIKE ? OR content LIKE ?) ORDER BY created_at
|
||||
DESC LIMIT ? OFFSET ?` — term wrapped as `%term%`, escaped (`%`, `_`).
|
||||
Visibility scoping mirrors ListPublic/ListMine (`public` + `viewer_id` for
|
||||
the saved-page variant).
|
||||
- Indexing: LIKE with a leading wildcard cannot use a B-tree index. Options,
|
||||
in order of effort:
|
||||
1. Accept a table scan — fine at ≤ ~50k rows (10k rows scanned in ~2 ms).
|
||||
2. Add an index on `title` for prefix search (`q*`) and keep `%q%` scan only
|
||||
as a fallback.
|
||||
3. SQLite FTS5 virtual table (`CREATE VIRTUAL TABLE pastes_fts USING
|
||||
fts5(title, content)`) for token search — best relevance, needs sync on
|
||||
insert/delete and a migration.
|
||||
- Cans: search should cover can titles/descriptions too (UNION ALL with
|
||||
`paste_cans`, `is_can=1`), matching the #4 listing integration.
|
||||
- Response shape: same row objects as `/api/public` (plus `is_can`) so
|
||||
`table.js` can render results without a second code path; the client filter
|
||||
becomes a server query when `q` is non-empty.
|
||||
@@ -172,6 +172,11 @@ func (a *apiServer) adminKeyOK(r *http.Request, key string) bool {
|
||||
|
||||
func (a *apiServer) adminAuth(next http.HandlerFunc, key string) http.HandlerFunc {
|
||||
return func(w http.ResponseWriter, r *http.Request) {
|
||||
if !rateLimitAdmin(r) {
|
||||
log.Printf("admin auth RATE LIMITED: %s %s from %s", r.Method, r.URL.Path, r.RemoteAddr)
|
||||
writeRateLimited(w, 60)
|
||||
return
|
||||
}
|
||||
if !a.adminKeyOK(r, key) {
|
||||
log.Printf("admin auth FAILURE: %s %s from %s", r.Method, r.URL.Path, r.RemoteAddr)
|
||||
writeErr(w, 401, "unauthorized")
|
||||
|
||||
@@ -0,0 +1,80 @@
|
||||
package api
|
||||
|
||||
// #66: admin key attempts must be rate limited per IP (5/min), constant-time
|
||||
// compared, and failures logged. Hammering bad keys must yield 429s.
|
||||
|
||||
import (
|
||||
"net/http/httptest"
|
||||
"strings"
|
||||
"testing"
|
||||
)
|
||||
|
||||
// TestAdminKeyRateLimited: burst of 5 bad-key attempts allowed (401), the 6th
|
||||
// gets 429, and even the correct key is blocked from that IP until refill.
|
||||
func TestAdminKeyRateLimited(t *testing.T) {
|
||||
srv := newTestServer(t)
|
||||
h := srv.routes()
|
||||
reqIP := "10.7.7.1:1234"
|
||||
|
||||
var got429, retryAfter bool
|
||||
var lastCode int
|
||||
for i := 0; i < 10; i++ {
|
||||
req := httptest.NewRequest("POST", "/admin/api/settings", nil)
|
||||
req.RemoteAddr = reqIP
|
||||
req.Header.Set("X-Admin-Key", "wrong-key")
|
||||
rec := httptest.NewRecorder()
|
||||
h.ServeHTTP(rec, req)
|
||||
lastCode = rec.Code
|
||||
if rec.Code == 429 {
|
||||
got429 = true
|
||||
retryAfter = rec.Header().Get("Retry-After") != ""
|
||||
break
|
||||
}
|
||||
}
|
||||
if !got429 {
|
||||
t.Fatalf("expected 429 after hammering bad keys, last status %d", lastCode)
|
||||
}
|
||||
if !retryAfter {
|
||||
t.Error("429 missing Retry-After header")
|
||||
}
|
||||
|
||||
// Correct key from the same IP is also locked out.
|
||||
req := httptest.NewRequest("POST", "/admin/api/settings", nil)
|
||||
req.RemoteAddr = reqIP
|
||||
req.Header.Set("X-Admin-Key", srv.adminKey)
|
||||
rec := httptest.NewRecorder()
|
||||
h.ServeHTTP(rec, req)
|
||||
if rec.Code != 429 {
|
||||
t.Errorf("correct key after lockout: got %d, want 429", rec.Code)
|
||||
}
|
||||
|
||||
// A different IP is unaffected.
|
||||
req2 := httptest.NewRequest("POST", "/admin/api/settings", strings.NewReader(`{"rate_limit_burst":5,"rate_limit_per_minute":60,"max_content_bytes":1048576,"custom_slug_reservation_days":30,"burn_viewer_window_minutes":15}`))
|
||||
req2.RemoteAddr = "203.0.113.9:1234"
|
||||
req2.Header.Set("X-Admin-Key", srv.adminKey)
|
||||
rec2 := httptest.NewRecorder()
|
||||
h.ServeHTTP(rec2, req2)
|
||||
if rec2.Code != 200 {
|
||||
t.Errorf("correct key from another IP: got %d, want 200", rec2.Code)
|
||||
}
|
||||
}
|
||||
|
||||
// TestAdminKeyConstantTimeCompare: sanity check that the comparison is
|
||||
// constant-time (uses subtle.ConstantTimeCompare, not ==).
|
||||
func TestAdminKeyConstantTimeCompare(t *testing.T) {
|
||||
srv := newTestServer(t)
|
||||
r := httptest.NewRequest("GET", "/", nil)
|
||||
r.Header.Set("X-Admin-Key", "test-admin-key")
|
||||
if !srv.adminKeyOK(r, srv.adminKey) {
|
||||
t.Fatal("correct key rejected")
|
||||
}
|
||||
r.Header.Set("X-Admin-Key", "wrong")
|
||||
if srv.adminKeyOK(r, srv.adminKey) {
|
||||
t.Fatal("wrong key accepted")
|
||||
}
|
||||
// differ in length: must not panic/mismatch unexpectedly
|
||||
r.Header.Set("X-Admin-Key", "test-admin-key-longer")
|
||||
if srv.adminKeyOK(r, srv.adminKey) {
|
||||
t.Fatal("longer wrong key accepted")
|
||||
}
|
||||
}
|
||||
@@ -46,6 +46,33 @@ func getWithCookie(t *testing.T, h anyHandler, id, viewer string) *httptest.Resp
|
||||
return rec
|
||||
}
|
||||
|
||||
// #82: burn_after_reads > 0 alone must enable burn-after-read
|
||||
// even without burn_after_read: true.
|
||||
func TestBurnReadsImpliedByBurnAfterReads(t *testing.T) {
|
||||
s := testServer(t)
|
||||
h := s.routes()
|
||||
req := httptest.NewRequest("POST", "/api/pastes", strings.NewReader(`{"content":"implied","burn_after_reads":2}`))
|
||||
rec := httptest.NewRecorder()
|
||||
h.ServeHTTP(rec, req)
|
||||
if rec.Code != 201 {
|
||||
t.Fatalf("create burn_after_reads-only: %d %s", rec.Code, rec.Body.String())
|
||||
}
|
||||
var created struct {
|
||||
ID string `json:"id"`
|
||||
}
|
||||
json.Unmarshal(rec.Body.Bytes(), &created)
|
||||
|
||||
if rec := getWithCookie(t, h, created.ID, "aaa"); rec.Code != 200 {
|
||||
t.Fatalf("read 1: %d", rec.Code)
|
||||
}
|
||||
if rec := getWithCookie(t, h, created.ID, "bbb"); rec.Code != 200 {
|
||||
t.Fatalf("read 2: %d", rec.Code)
|
||||
}
|
||||
if rec := getWithCookie(t, h, created.ID, "ccc"); rec.Code != 404 {
|
||||
t.Fatalf("read 3 expected 404 (burned), got %d", rec.Code)
|
||||
}
|
||||
}
|
||||
|
||||
func TestBurnAfterNReadsDistinctViewers(t *testing.T) {
|
||||
s := testServer(t)
|
||||
h := s.routes()
|
||||
|
||||
@@ -28,7 +28,7 @@ func (a *apiServer) handleCreateCan(w http.ResponseWriter, r *http.Request) {
|
||||
visibility = "public"
|
||||
}
|
||||
if visibility != "public" && visibility != "unlisted" {
|
||||
writeErr(w, 400, "visibility must be public or unlisted")
|
||||
writeErrCode(w, 400, "invalid_visibility", "visibility must be public or unlisted")
|
||||
return
|
||||
}
|
||||
expiresIn := r.FormValue("expires_in")
|
||||
@@ -40,13 +40,13 @@ func (a *apiServer) handleCreateCan(w http.ResponseWriter, r *http.Request) {
|
||||
if expiresIn != "" {
|
||||
d, err := time.ParseDuration(expiresIn)
|
||||
if err != nil {
|
||||
writeErr(w, 400, "invalid expires_in")
|
||||
writeErrCode(w, 400, "expiry_invalid", "invalid expires_in")
|
||||
return
|
||||
}
|
||||
// #60/#48: clamp at the API boundary like the pastes API does -
|
||||
// reject zero/negative and durations past the 1-year UI cap.
|
||||
if !store.ValidExpiry(d) {
|
||||
writeErr(w, 400, "expires_in must be between 1 minute and 1 year")
|
||||
writeErrCode(w, 400, "expiry_invalid", "expires_in must be between 1 minute and 1 year")
|
||||
return
|
||||
}
|
||||
t := now + int64(d.Seconds())
|
||||
@@ -71,7 +71,7 @@ func (a *apiServer) handleCreateCan(w http.ResponseWriter, r *http.Request) {
|
||||
if err != nil {
|
||||
switch err {
|
||||
case store.ErrSlugTaken, store.ErrInvalidSlug, store.ErrReservedSlug:
|
||||
writeErr(w, 409, err.Error())
|
||||
writeErrCode(w, 409, createErrCode(err), err.Error())
|
||||
default:
|
||||
writeErr(w, 500, "db error")
|
||||
}
|
||||
@@ -137,7 +137,7 @@ func (a *apiServer) handleCreateCan(w http.ResponseWriter, r *http.Request) {
|
||||
|
||||
if itemCount == 0 {
|
||||
a.store.DeleteCan(canID)
|
||||
writeErr(w, 400, "can needs at least one item (files or json_items)")
|
||||
writeErrCode(w, 400, "content_empty", "can needs at least one item (files or json_items)")
|
||||
return
|
||||
}
|
||||
|
||||
|
||||
@@ -0,0 +1,45 @@
|
||||
package api
|
||||
|
||||
import (
|
||||
"net/http/httptest"
|
||||
"testing"
|
||||
)
|
||||
|
||||
// #60: the cans API must clamp expires_in at the boundary exactly like the
|
||||
// pastes API — reject zero/negative durations and anything over the 1-year
|
||||
// UI cap, accept the exact boundaries.
|
||||
func TestCreateCanExpiryBounds(t *testing.T) {
|
||||
s := testServer(t)
|
||||
h := s.routes()
|
||||
|
||||
cases := []struct {
|
||||
expiresIn string
|
||||
wantCode int
|
||||
}{
|
||||
{"-1h", 400}, // negative
|
||||
{"-0s", 400}, // negative zero
|
||||
{"0s", 400}, // zero
|
||||
{"1ns", 400}, // positive but below the 1-minute floor
|
||||
{"59s", 400}, // just under the floor
|
||||
{"1m", 201}, // exactly the floor
|
||||
{"90s", 201}, // just over the floor
|
||||
{"8760h", 201}, // exactly 1 year
|
||||
{"8785h", 400}, // 1 year + 1 day: over the cap
|
||||
{"87600h", 400}, // 10 years, the originally reported case
|
||||
}
|
||||
for _, c := range cases {
|
||||
globalLimiter = newLimiter() // avoid create rate limit between cases
|
||||
body, ct := multipartBody(t, map[string]string{
|
||||
"json_items": `[{"title":"a.txt","content":"AAA"}]`,
|
||||
"expires_in": c.expiresIn,
|
||||
}, "files", "pic.txt", "file data")
|
||||
req := httptest.NewRequest("POST", "/api/pastes/can", body)
|
||||
req.Header.Set("Content-Type", ct)
|
||||
rec := httptest.NewRecorder()
|
||||
h.ServeHTTP(rec, req)
|
||||
if rec.Code != c.wantCode {
|
||||
t.Errorf("expires_in %q: got %d want %d (%s)",
|
||||
c.expiresIn, rec.Code, c.wantCode, rec.Body.String())
|
||||
}
|
||||
}
|
||||
}
|
||||
@@ -0,0 +1,123 @@
|
||||
package api
|
||||
|
||||
import (
|
||||
"encoding/json"
|
||||
"net/http"
|
||||
"net/http/httptest"
|
||||
"strings"
|
||||
"testing"
|
||||
)
|
||||
|
||||
// #105: every validation path on create returns a machine-readable `code`
|
||||
// alongside the human `error` message, so the new-page JS can map known
|
||||
// codes to plain-language guidance.
|
||||
|
||||
func decodeErr(t *testing.T, rec *httptest.ResponseRecorder) (status int, errMsg, code string) {
|
||||
t.Helper()
|
||||
var got struct {
|
||||
Error string `json:"error"`
|
||||
Code string `json:"code"`
|
||||
}
|
||||
if err := json.Unmarshal(rec.Body.Bytes(), &got); err != nil {
|
||||
t.Fatalf("bad json: %v (%s)", err, rec.Body.String())
|
||||
}
|
||||
return rec.Code, got.Error, got.Code
|
||||
}
|
||||
|
||||
func postCreate(h http.Handler, body string) *httptest.ResponseRecorder {
|
||||
req := httptest.NewRequest("POST", "/api/pastes", strings.NewReader(body))
|
||||
rec := httptest.NewRecorder()
|
||||
h.ServeHTTP(rec, req)
|
||||
return rec
|
||||
}
|
||||
|
||||
func TestErrorCodeContentEmpty(t *testing.T) {
|
||||
h := testServer(t).routes()
|
||||
_, _, code := decodeErr(t, postCreate(h, `{"content":" "}`))
|
||||
if code != "content_empty" {
|
||||
t.Fatalf("code = %q, want content_empty", code)
|
||||
}
|
||||
}
|
||||
|
||||
func TestErrorCodeContentTooLarge(t *testing.T) {
|
||||
h := testServer(t).routes()
|
||||
big := strings.Repeat("x", 6*1024*1024) // over the 5MB test cap
|
||||
_, _, code := decodeErr(t, postCreate(h, `{"content":"`+big+`"}`))
|
||||
if code != "content_too_large" {
|
||||
t.Fatalf("code = %q, want content_too_large", code)
|
||||
}
|
||||
}
|
||||
|
||||
func TestErrorCodeSlugTaken(t *testing.T) {
|
||||
h := testServer(t).routes()
|
||||
if rec := postCreate(h, `{"content":"a","custom_slug":"taken-slug"}`); rec.Code != 201 {
|
||||
t.Fatalf("seed create: %d %s", rec.Code, rec.Body.String())
|
||||
}
|
||||
_, _, code := decodeErr(t, postCreate(h, `{"content":"b","custom_slug":"taken-slug"}`))
|
||||
if code != "slug_taken" {
|
||||
t.Fatalf("code = %q, want slug_taken", code)
|
||||
}
|
||||
}
|
||||
|
||||
func TestErrorCodeSlugInvalid(t *testing.T) {
|
||||
h := testServer(t).routes()
|
||||
_, _, code := decodeErr(t, postCreate(h, `{"content":"a","custom_slug":"bad slug!"}`))
|
||||
if code != "slug_invalid" {
|
||||
t.Fatalf("code = %q, want slug_invalid", code)
|
||||
}
|
||||
}
|
||||
|
||||
func TestErrorCodeExpiryInvalid(t *testing.T) {
|
||||
h := testServer(t).routes()
|
||||
_, _, code := decodeErr(t, postCreate(h, `{"content":"a","expires_in":"2s"}`))
|
||||
if code != "expiry_invalid" {
|
||||
t.Fatalf("code = %q, want expiry_invalid", code)
|
||||
}
|
||||
}
|
||||
|
||||
func TestErrorCodeRateLimited(t *testing.T) {
|
||||
h := testServer(t).routes()
|
||||
var code string
|
||||
for i := 0; i < 20; i++ {
|
||||
_, _, code = decodeErr(t, postCreate(h, `{"content":"a"}`))
|
||||
if code == "rate_limited" {
|
||||
return
|
||||
}
|
||||
}
|
||||
t.Fatalf("never got rate_limited, last code = %q", code)
|
||||
}
|
||||
|
||||
func TestErrorCodeCanValidation(t *testing.T) {
|
||||
h := testServer(t).routes()
|
||||
|
||||
post := func(fields map[string]string) *httptest.ResponseRecorder {
|
||||
var b strings.Builder
|
||||
for k, v := range fields {
|
||||
b.WriteString("--B\r\nContent-Disposition: form-data; name=\"" + k + "\"\r\n\r\n" + v + "\r\n")
|
||||
}
|
||||
b.WriteString("--B--\r\n")
|
||||
req := httptest.NewRequest("POST", "/api/pastes/can", strings.NewReader(b.String()))
|
||||
req.Header.Set("Content-Type", "multipart/form-data; boundary=B")
|
||||
rec := httptest.NewRecorder()
|
||||
h.ServeHTTP(rec, req)
|
||||
return rec
|
||||
}
|
||||
|
||||
// bad visibility
|
||||
if _, _, code := decodeErr(t, post(map[string]string{"title": "x", "visibility": "nope"})); code != "invalid_visibility" {
|
||||
t.Fatalf("visibility code = %q, want invalid_visibility", code)
|
||||
}
|
||||
|
||||
// invalid expiry
|
||||
if _, _, code := decodeErr(t, post(map[string]string{"title": "x", "expires_in": "1s"})); code != "expiry_invalid" {
|
||||
t.Fatalf("expiry code = %q, want expiry_invalid", code)
|
||||
}
|
||||
|
||||
// slug taken on can create
|
||||
if rec := postCreate(h, `{"content":"a","custom_slug":"can-slug"}`); rec.Code != 201 {
|
||||
t.Fatalf("seed create: %d", rec.Code)
|
||||
}
|
||||
if _, _, code := decodeErr(t, post(map[string]string{"title": "x", "custom_slug": "can-slug", "json_items": `[{"title":"a","content":"b"}]`})); code != "slug_taken" {
|
||||
t.Fatalf("can slug code = %q, want slug_taken", code)
|
||||
}
|
||||
}
|
||||
@@ -0,0 +1,198 @@
|
||||
package api
|
||||
|
||||
// Regression tests for #68 input-validation gaps: negative/oversized content
|
||||
// lengths (413), limit=0 → default page size, unchecked query params
|
||||
// (negative offset), and negative burn_after_reads.
|
||||
|
||||
import (
|
||||
"encoding/json"
|
||||
"fmt"
|
||||
"net/http"
|
||||
"net/http/httptest"
|
||||
"strings"
|
||||
"testing"
|
||||
)
|
||||
|
||||
func createPasteRaw(t *testing.T, h http.Handler, body string) *httptest.ResponseRecorder {
|
||||
t.Helper()
|
||||
req := httptest.NewRequest("POST", "/api/pastes", strings.NewReader(body))
|
||||
rec := httptest.NewRecorder()
|
||||
h.ServeHTTP(rec, req)
|
||||
return rec
|
||||
}
|
||||
|
||||
// A request whose decoded content exceeds the admin-tunable cap is rejected
|
||||
// with 413 and a clear message (content under the body cap, over the
|
||||
// content cap).
|
||||
func TestCreatePasteContentOverCap413(t *testing.T) {
|
||||
s := testServer(t)
|
||||
h := s.routes()
|
||||
|
||||
// content over MaxContentBytes (5MiB) but under body cap (+4KiB): send
|
||||
// just over the content cap so the per-field check fires first.
|
||||
content := strings.Repeat("a", 5*1024*1024+10)
|
||||
rec := createPasteRaw(t, h, fmt.Sprintf(`{"content":"%s"}`, content))
|
||||
if rec.Code != http.StatusRequestEntityTooLarge {
|
||||
t.Fatalf("got %d want 413: %s", rec.Code, rec.Body.String())
|
||||
}
|
||||
if !strings.Contains(rec.Body.String(), "content exceeds max") {
|
||||
t.Fatalf("unclear error message: %s", rec.Body.String())
|
||||
}
|
||||
}
|
||||
|
||||
// A request whose entire body is larger than the server-side body cap is cut
|
||||
// off by http.MaxBytesReader and answered with 413, not decoded into memory
|
||||
// (#68: previously a giant body was fully buffered, then rejected only at
|
||||
// the per-field check — actually the decode happened before any check).
|
||||
func TestCreatePasteBodyOverCap413(t *testing.T) {
|
||||
s := testServer(t)
|
||||
// shrink the content cap so the body cap is small too
|
||||
ss := s.settings.get()
|
||||
ss.MaxContentBytes = 64 * 1024
|
||||
if err := s.settings.set(ss); err != nil {
|
||||
t.Fatal(err)
|
||||
}
|
||||
h := s.routes()
|
||||
|
||||
content := strings.Repeat("a", 200*1024) // 200KiB > 64KiB+4KiB body cap
|
||||
rec := createPasteRaw(t, h, fmt.Sprintf(`{"content":"%s","title":"x"}`, content))
|
||||
if rec.Code != http.StatusRequestEntityTooLarge {
|
||||
t.Fatalf("got %d want 413: %s", rec.Code, rec.Body.String())
|
||||
}
|
||||
}
|
||||
|
||||
// Negative content lengths cannot be expressed via JSON, but a negative
|
||||
// expires-style numeric payload must not crash; more importantly the
|
||||
// burn_after_reads field: negative values are rejected with a clear message.
|
||||
func TestCreatePasteNegativeBurnAfterReads(t *testing.T) {
|
||||
s := testServer(t)
|
||||
h := s.routes()
|
||||
|
||||
rec := createPasteRaw(t, h, `{"content":"hi","burn_after_reads":-5}`)
|
||||
if rec.Code != http.StatusBadRequest {
|
||||
t.Fatalf("got %d want 400: %s", rec.Code, rec.Body.String())
|
||||
}
|
||||
if !strings.Contains(rec.Body.String(), "burn_after_reads") {
|
||||
t.Fatalf("unclear error message: %s", rec.Body.String())
|
||||
}
|
||||
|
||||
// 0 and positive values still work (0 = default single read, per #49)
|
||||
rec = createPasteRaw(t, h, `{"content":"hi","burn_after_reads":0,"burn_after_read":true}`)
|
||||
if rec.Code != http.StatusCreated {
|
||||
t.Fatalf("zero burn_after_reads: got %d want 201: %s", rec.Code, rec.Body.String())
|
||||
}
|
||||
}
|
||||
|
||||
// limit=0 on list endpoints returns the default page size (existing clamp
|
||||
// treats <=0 as default; #68 asks this be explicit and tested).
|
||||
func TestListLimitZeroUsesDefault(t *testing.T) {
|
||||
s := testServer(t)
|
||||
h := s.routes()
|
||||
|
||||
// seed 3 public pastes
|
||||
for i := 0; i < 3; i++ {
|
||||
rec := createPasteRaw(t, h, fmt.Sprintf(`{"content":"p%d"}`, i))
|
||||
if rec.Code != 201 {
|
||||
t.Fatalf("seed: got %d: %s", rec.Code, rec.Body.String())
|
||||
}
|
||||
}
|
||||
|
||||
for _, q := range []string{"/api/public?limit=0", "/api/public"} {
|
||||
req := httptest.NewRequest("GET", q, nil)
|
||||
rec := httptest.NewRecorder()
|
||||
h.ServeHTTP(rec, req)
|
||||
if rec.Code != 200 {
|
||||
t.Fatalf("%s: got %d", q, rec.Code)
|
||||
}
|
||||
var got struct {
|
||||
Limit int `json:"limit"`
|
||||
Total int `json:"total"`
|
||||
Items []struct{ ID string } `json:"items"`
|
||||
}
|
||||
json.Unmarshal(rec.Body.Bytes(), &got)
|
||||
if got.Limit != 25 || len(got.Items) != 3 {
|
||||
t.Fatalf("%s: limit=%d items=%d, want limit 25 and all 3 items", q, got.Limit, len(got.Items))
|
||||
}
|
||||
}
|
||||
}
|
||||
|
||||
// Huge limit values are clamped to the max page size (already the behavior;
|
||||
// regression-tested here per #68 "validate unchecked params").
|
||||
func TestListLimitHugeClamped(t *testing.T) {
|
||||
s := testServer(t)
|
||||
h := s.routes()
|
||||
|
||||
req := httptest.NewRequest("GET", "/api/public?limit=999999999", nil)
|
||||
rec := httptest.NewRecorder()
|
||||
h.ServeHTTP(rec, req)
|
||||
var got struct {
|
||||
Limit int `json:"limit"`
|
||||
}
|
||||
json.Unmarshal(rec.Body.Bytes(), &got)
|
||||
if got.Limit != 25 {
|
||||
t.Fatalf("limit=%d, want clamped to 25", got.Limit)
|
||||
}
|
||||
}
|
||||
|
||||
// Negative offset previously passed through unchecked to SQL (harmless in
|
||||
// SQLite, but invalid); it must be clamped to 0 (#68).
|
||||
func TestListNegativeOffsetClamped(t *testing.T) {
|
||||
s := testServer(t)
|
||||
h := s.routes()
|
||||
|
||||
for i := 0; i < 2; i++ {
|
||||
rec := createPasteRaw(t, h, fmt.Sprintf(`{"content":"p%d"}`, i))
|
||||
if rec.Code != 201 {
|
||||
t.Fatalf("seed: got %d", rec.Code)
|
||||
}
|
||||
}
|
||||
|
||||
req := httptest.NewRequest("GET", "/api/public?offset=-999", nil)
|
||||
rec := httptest.NewRecorder()
|
||||
h.ServeHTTP(rec, req)
|
||||
if rec.Code != 200 {
|
||||
t.Fatalf("got %d", rec.Code)
|
||||
}
|
||||
var got struct {
|
||||
Offset int `json:"offset"`
|
||||
Total int `json:"total"`
|
||||
}
|
||||
json.Unmarshal(rec.Body.Bytes(), &got)
|
||||
if got.Offset != 0 || got.Total != 2 {
|
||||
t.Fatalf("offset=%d total=%d, want offset 0 and total 2", got.Offset, got.Total)
|
||||
}
|
||||
|
||||
// /api/mine too (needs the viewer cookie)
|
||||
req = httptest.NewRequest("GET", "/api/mine?offset=-5", nil)
|
||||
req.AddCookie(&http.Cookie{Name: "vwr", Value: "offclamp"})
|
||||
rec = httptest.NewRecorder()
|
||||
h.ServeHTTP(rec, req)
|
||||
var mine struct {
|
||||
Offset int `json:"offset"`
|
||||
}
|
||||
json.Unmarshal(rec.Body.Bytes(), &mine)
|
||||
if mine.Offset != 0 {
|
||||
t.Fatalf("mine offset=%d, want 0", mine.Offset)
|
||||
}
|
||||
}
|
||||
|
||||
// Non-numeric limit/offset fall back to defaults instead of 500s.
|
||||
func TestListGarbageParams(t *testing.T) {
|
||||
s := testServer(t)
|
||||
h := s.routes()
|
||||
|
||||
req := httptest.NewRequest("GET", "/api/public?limit=abc&offset=xyz", nil)
|
||||
rec := httptest.NewRecorder()
|
||||
h.ServeHTTP(rec, req)
|
||||
if rec.Code != 200 {
|
||||
t.Fatalf("got %d", rec.Code)
|
||||
}
|
||||
var got struct {
|
||||
Limit int `json:"limit"`
|
||||
Offset int `json:"offset"`
|
||||
}
|
||||
json.Unmarshal(rec.Body.Bytes(), &got)
|
||||
if got.Limit != 25 || got.Offset != 0 {
|
||||
t.Fatalf("limit=%d offset=%d, want 25/0", got.Limit, got.Offset)
|
||||
}
|
||||
}
|
||||
@@ -0,0 +1,92 @@
|
||||
package api
|
||||
|
||||
// #81: ALL password verification attempts (GET query param, header, POST
|
||||
// form) must go through the per-IP unlock limiter. Regression: N wrong
|
||||
// passwords via GET ?password= must eventually yield 429.
|
||||
|
||||
import (
|
||||
"encoding/json"
|
||||
"net/http/httptest"
|
||||
"strings"
|
||||
"testing"
|
||||
)
|
||||
|
||||
func createPasswordPaste(t *testing.T, s *apiServer, pw string) string {
|
||||
t.Helper()
|
||||
h := s.routes()
|
||||
body := `{"content":"secret","password":"` + pw + `"}`
|
||||
req := httptest.NewRequest("POST", "/api/pastes", strings.NewReader(body))
|
||||
rec := httptest.NewRecorder()
|
||||
h.ServeHTTP(rec, req)
|
||||
var created struct {
|
||||
ID string `json:"id"`
|
||||
}
|
||||
json.Unmarshal(rec.Body.Bytes(), &created)
|
||||
return created.ID
|
||||
}
|
||||
|
||||
// TestRateLimitGetPasswordQuery: repeated wrong passwords via GET
|
||||
// ?password= must eventually return 429 (unlock limiter: burst 5).
|
||||
func TestRateLimitGetPasswordQuery(t *testing.T) {
|
||||
s := testServer(t)
|
||||
h := s.routes()
|
||||
id := createPasswordPaste(t, s, "hunter2")
|
||||
|
||||
var saw429 bool
|
||||
// more attempts than the unlock burst (5)
|
||||
for i := 0; i < 10; i++ {
|
||||
req := httptest.NewRequest("GET", "/api/pastes/"+id+"?password=wrong"+string(rune('a'+i)), nil)
|
||||
rec := httptest.NewRecorder()
|
||||
h.ServeHTTP(rec, req)
|
||||
if rec.Code == 429 {
|
||||
saw429 = true
|
||||
break
|
||||
}
|
||||
if rec.Code != 401 {
|
||||
t.Fatalf("attempt %d: expected 401 before limit, got %d", i, rec.Code)
|
||||
}
|
||||
}
|
||||
if !saw429 {
|
||||
t.Fatal("expected 429 after repeated wrong ?password= attempts, never got one")
|
||||
}
|
||||
}
|
||||
|
||||
// TestRateLimitGetPasswordHeader: same guarantee for the X-Paste-Password header path.
|
||||
func TestRateLimitGetPasswordHeader(t *testing.T) {
|
||||
s := testServer(t)
|
||||
h := s.routes()
|
||||
id := createPasswordPaste(t, s, "hunter2")
|
||||
|
||||
var saw429 bool
|
||||
for i := 0; i < 10; i++ {
|
||||
req := httptest.NewRequest("GET", "/api/pastes/"+id, nil)
|
||||
req.Header.Set("X-Paste-Password", "wrong"+string(rune('a'+i)))
|
||||
rec := httptest.NewRecorder()
|
||||
h.ServeHTTP(rec, req)
|
||||
if rec.Code == 429 {
|
||||
saw429 = true
|
||||
break
|
||||
}
|
||||
if rec.Code != 401 {
|
||||
t.Fatalf("attempt %d: expected 401 before limit, got %d", i, rec.Code)
|
||||
}
|
||||
}
|
||||
if !saw429 {
|
||||
t.Fatal("expected 429 after repeated wrong header password attempts, never got one")
|
||||
}
|
||||
}
|
||||
|
||||
// TestRateLimitGetPasswordCorrectStillAllowed: a correct password must still
|
||||
// work within the burst (the limiter gates attempts, not correctness).
|
||||
func TestRateLimitGetPasswordCorrectStillAllowed(t *testing.T) {
|
||||
s := testServer(t)
|
||||
h := s.routes()
|
||||
id := createPasswordPaste(t, s, "hunter2")
|
||||
|
||||
req := httptest.NewRequest("GET", "/api/pastes/"+id+"?password=hunter2", nil)
|
||||
rec := httptest.NewRecorder()
|
||||
h.ServeHTTP(rec, req)
|
||||
if rec.Code != 200 {
|
||||
t.Fatalf("expected 200 for correct password within burst, got %d", rec.Code)
|
||||
}
|
||||
}
|
||||
@@ -0,0 +1,152 @@
|
||||
package api
|
||||
|
||||
// Regression tests for #86: title and language are bounded at create time.
|
||||
// Titles over 200 chars are truncated; language must match
|
||||
// ^[a-zA-Z0-9+#-]{1,40}$ or the create is rejected with a clear 400.
|
||||
|
||||
import (
|
||||
"encoding/json"
|
||||
"net/http"
|
||||
"net/http/httptest"
|
||||
"strings"
|
||||
"testing"
|
||||
)
|
||||
|
||||
// pasteMeta fetches a created paste's stored metadata via the API.
|
||||
func pasteMeta(t *testing.T, h http.Handler, id string) map[string]any {
|
||||
t.Helper()
|
||||
rec := httptest.NewRecorder()
|
||||
h.ServeHTTP(rec, httptest.NewRequest("GET", "/api/pastes/"+id, nil))
|
||||
if rec.Code != 200 {
|
||||
t.Fatalf("get paste %s: got %d: %s", id, rec.Code, rec.Body.String())
|
||||
}
|
||||
var m map[string]any
|
||||
if err := json.Unmarshal(rec.Body.Bytes(), &m); err != nil {
|
||||
t.Fatal(err)
|
||||
}
|
||||
return m
|
||||
}
|
||||
|
||||
// A 5000-char title is truncated to 200 characters at create time (#86).
|
||||
func TestCreatePasteTitleTruncated(t *testing.T) {
|
||||
s := testServer(t)
|
||||
h := s.routes()
|
||||
|
||||
title := strings.Repeat("t", 5000)
|
||||
body, _ := json.Marshal(map[string]any{"content": "hi", "title": title})
|
||||
rec := createPasteRaw(t, h, string(body))
|
||||
if rec.Code != http.StatusCreated {
|
||||
t.Fatalf("got %d want 201: %s", rec.Code, rec.Body.String())
|
||||
}
|
||||
var resp struct {
|
||||
ID string `json:"id"`
|
||||
}
|
||||
json.Unmarshal(rec.Body.Bytes(), &resp)
|
||||
meta := pasteMeta(t, h, resp.ID)
|
||||
got, _ := meta["title"].(string)
|
||||
if got != strings.Repeat("t", 200) {
|
||||
t.Fatalf("title not truncated to 200 chars: len=%d", len(got))
|
||||
}
|
||||
}
|
||||
|
||||
// A title within the 200-char bound is stored verbatim (minus surrounding
|
||||
// whitespace, which is trimmed).
|
||||
func TestCreatePasteTitleWithinBoundKept(t *testing.T) {
|
||||
s := testServer(t)
|
||||
h := s.routes()
|
||||
|
||||
title := " " + strings.Repeat("x", 200) + " "
|
||||
body, _ := json.Marshal(map[string]any{"content": "hi", "title": title})
|
||||
rec := createPasteRaw(t, h, string(body))
|
||||
if rec.Code != http.StatusCreated {
|
||||
t.Fatalf("got %d want 201: %s", rec.Code, rec.Body.String())
|
||||
}
|
||||
var resp struct {
|
||||
ID string `json:"id"`
|
||||
}
|
||||
json.Unmarshal(rec.Body.Bytes(), &resp)
|
||||
meta := pasteMeta(t, h, resp.ID)
|
||||
if got, _ := meta["title"].(string); got != strings.Repeat("x", 200) {
|
||||
t.Fatalf("title changed unexpectedly: len=%d", len(got))
|
||||
}
|
||||
}
|
||||
|
||||
// A language longer than 40 chars is rejected with a clear 400 (#86).
|
||||
func TestCreatePasteLanguageTooLong400(t *testing.T) {
|
||||
s := testServer(t)
|
||||
h := s.routes()
|
||||
|
||||
body, _ := json.Marshal(map[string]any{"content": "hi", "language": strings.Repeat("a", 41)})
|
||||
rec := createPasteRaw(t, h, string(body))
|
||||
if rec.Code != http.StatusBadRequest {
|
||||
t.Fatalf("got %d want 400: %s", rec.Code, rec.Body.String())
|
||||
}
|
||||
if !strings.Contains(rec.Body.String(), "language") {
|
||||
t.Fatalf("unclear error message: %s", rec.Body.String())
|
||||
}
|
||||
}
|
||||
|
||||
// Language strings outside ^[a-zA-Z0-9+#-]{1,40}$ are rejected with 400.
|
||||
func TestCreatePasteLanguageBadFormat400(t *testing.T) {
|
||||
s := testServer(t)
|
||||
h := s.routes()
|
||||
|
||||
for _, bad := range []string{
|
||||
"<img src=x onerror=alert(1)>",
|
||||
"java script",
|
||||
"c++ extra!",
|
||||
"py_thon",
|
||||
"go.lang",
|
||||
} {
|
||||
body, _ := json.Marshal(map[string]any{"content": "hi", "language": bad})
|
||||
rec := createPasteRaw(t, h, string(body))
|
||||
if rec.Code != http.StatusBadRequest {
|
||||
t.Errorf("language %q: got %d want 400: %s", bad, rec.Code, rec.Body.String())
|
||||
continue
|
||||
}
|
||||
if !strings.Contains(rec.Body.String(), "language must match") {
|
||||
t.Errorf("language %q: unclear error: %s", bad, rec.Body.String())
|
||||
}
|
||||
}
|
||||
}
|
||||
|
||||
// Valid languages (letters, digits, #, +, -) within 40 chars are accepted.
|
||||
func TestCreatePasteLanguageValidAccepted(t *testing.T) {
|
||||
for _, ok := range []string{"go", "c#", "f#", "c++", "objective-c", "ECMAScript-2023", strings.Repeat("a", 40)} {
|
||||
s2 := testServer(t) // fresh rate limiter per case
|
||||
h2 := s2.routes()
|
||||
body, _ := json.Marshal(map[string]any{"content": "hi", "language": ok})
|
||||
rec := createPasteRaw(t, h2, string(body))
|
||||
if rec.Code != http.StatusCreated {
|
||||
t.Errorf("language %q: got %d want 201: %s", ok, rec.Code, rec.Body.String())
|
||||
}
|
||||
}
|
||||
}
|
||||
|
||||
// An absent or blank language still creates fine and stores NULL, and a
|
||||
// blank title is stored NULL rather than an empty string.
|
||||
func TestCreatePasteBlankMetadataOK(t *testing.T) {
|
||||
s := testServer(t)
|
||||
h := s.routes()
|
||||
|
||||
for _, body := range []string{
|
||||
`{"content":"hi"}`,
|
||||
`{"content":"hi","language":"","title":" "}`,
|
||||
} {
|
||||
rec := createPasteRaw(t, h, body)
|
||||
if rec.Code != http.StatusCreated {
|
||||
t.Fatalf("body %s: got %d want 201: %s", body, rec.Code, rec.Body.String())
|
||||
}
|
||||
var resp struct {
|
||||
ID string `json:"id"`
|
||||
}
|
||||
json.Unmarshal(rec.Body.Bytes(), &resp)
|
||||
meta := pasteMeta(t, h, resp.ID)
|
||||
if lang, ok := meta["language"]; ok && lang != nil && lang != "" {
|
||||
t.Fatalf("body %s: language not null: %v", body, lang)
|
||||
}
|
||||
if title, ok := meta["title"]; ok && title != nil && title != "" {
|
||||
t.Fatalf("body %s: title not null: %v", body, title)
|
||||
}
|
||||
}
|
||||
}
|
||||
@@ -183,6 +183,46 @@ func TestListPublicExcludesUnlisted(t *testing.T) {
|
||||
}
|
||||
}
|
||||
|
||||
func TestListPublicExcludesPasswordAndUnlisted(t *testing.T) {
|
||||
s := testServer(t)
|
||||
h := s.routes()
|
||||
|
||||
bodies := []string{
|
||||
`{"content":"open","visibility":"public"}`,
|
||||
`{"content":"locked","visibility":"public","password":"hunter2"}`,
|
||||
`{"content":"hidden","visibility":"unlisted"}`,
|
||||
}
|
||||
for _, body := range bodies {
|
||||
req := httptest.NewRequest("POST", "/api/pastes", strings.NewReader(body))
|
||||
rec := httptest.NewRecorder()
|
||||
h.ServeHTTP(rec, req)
|
||||
if rec.Code != 201 {
|
||||
t.Fatalf("create %s: got %d", body, rec.Code)
|
||||
}
|
||||
}
|
||||
|
||||
req := httptest.NewRequest("GET", "/api/public", nil)
|
||||
rec := httptest.NewRecorder()
|
||||
h.ServeHTTP(rec, req)
|
||||
if rec.Code != 200 {
|
||||
t.Fatalf("list public: got %d", rec.Code)
|
||||
}
|
||||
var resp struct {
|
||||
Total int `json:"total"`
|
||||
Items []map[string]any `json:"items"`
|
||||
}
|
||||
json.Unmarshal(rec.Body.Bytes(), &resp)
|
||||
if resp.Total != 1 || len(resp.Items) != 1 {
|
||||
t.Fatalf("expected only the 1 public paste, got total=%d items=%d", resp.Total, len(resp.Items))
|
||||
}
|
||||
// password-protected and unlisted pastes must not appear (no metadata leak)
|
||||
for _, secret := range []string{"hunter2", "locked", "hidden"} {
|
||||
if strings.Contains(rec.Body.String(), secret) {
|
||||
t.Fatalf("leaked %q in /api/public response", secret)
|
||||
}
|
||||
}
|
||||
}
|
||||
|
||||
func TestSweepSoftDeletesAfterGrace(t *testing.T) {
|
||||
s := testServer(t)
|
||||
h := s.routes()
|
||||
|
||||
@@ -0,0 +1,97 @@
|
||||
package api
|
||||
|
||||
// #83 regression tests: `public` boolean in the create payload must map to
|
||||
// visibility (false -> unlisted, true -> public); string `visibility` still works.
|
||||
|
||||
import (
|
||||
"encoding/json"
|
||||
"net/http/httptest"
|
||||
"strings"
|
||||
"testing"
|
||||
)
|
||||
|
||||
func createPasteBody(t *testing.T, h *apiServer, body string) map[string]any {
|
||||
req := httptest.NewRequest("POST", "/api/pastes", strings.NewReader(body))
|
||||
rec := httptest.NewRecorder()
|
||||
h.routes().ServeHTTP(rec, req)
|
||||
if rec.Code != 201 {
|
||||
t.Fatalf("create: got %d: %s", rec.Code, rec.Body.String())
|
||||
}
|
||||
var resp map[string]any
|
||||
if err := json.Unmarshal(rec.Body.Bytes(), &resp); err != nil {
|
||||
t.Fatalf("bad json: %v", err)
|
||||
}
|
||||
return resp
|
||||
}
|
||||
|
||||
func getVis(t *testing.T, h *apiServer, id string) string {
|
||||
req := httptest.NewRequest("GET", "/api/pastes/"+id, nil)
|
||||
rec := httptest.NewRecorder()
|
||||
h.routes().ServeHTTP(rec, req)
|
||||
if rec.Code != 200 {
|
||||
t.Fatalf("get %s: got %d", id, rec.Code)
|
||||
}
|
||||
var resp struct {
|
||||
Visibility string `json:"visibility"`
|
||||
}
|
||||
if err := json.Unmarshal(rec.Body.Bytes(), &resp); err != nil {
|
||||
t.Fatalf("bad json: %v", err)
|
||||
}
|
||||
return resp.Visibility
|
||||
}
|
||||
|
||||
// TestPublicBooleanFalseMapsToUnlisted: {"public": false} must create an unlisted paste.
|
||||
func TestPublicBooleanFalseMapsToUnlisted(t *testing.T) {
|
||||
s := testServer(t)
|
||||
resp := createPasteBody(t, s, `{"content":"x","public":false}`)
|
||||
if v := getVis(t, s, resp["id"].(string)); v != "unlisted" {
|
||||
t.Fatalf("public:false -> got visibility %q, want unlisted", v)
|
||||
}
|
||||
}
|
||||
|
||||
// TestPublicBooleanTrueMapsToPublic: {"public": true} must create a public paste.
|
||||
func TestPublicBooleanTrueMapsToPublic(t *testing.T) {
|
||||
s := testServer(t)
|
||||
resp := createPasteBody(t, s, `{"content":"x","public":true}`)
|
||||
if v := getVis(t, s, resp["id"].(string)); v != "public" {
|
||||
t.Fatalf("public:true -> got visibility %q, want public", v)
|
||||
}
|
||||
}
|
||||
|
||||
// TestPublicBooleanOverridesString: boolean wins when both fields are sent.
|
||||
func TestPublicBooleanOverridesString(t *testing.T) {
|
||||
s := testServer(t)
|
||||
resp := createPasteBody(t, s, `{"content":"x","visibility":"public","public":false}`)
|
||||
if v := getVis(t, s, resp["id"].(string)); v != "unlisted" {
|
||||
t.Fatalf("boolean override -> got %q, want unlisted", v)
|
||||
}
|
||||
}
|
||||
|
||||
// TestVisibilityStringStillWorks: existing string contract unchanged.
|
||||
func TestVisibilityStringStillWorks(t *testing.T) {
|
||||
s := testServer(t)
|
||||
resp := createPasteBody(t, s, `{"content":"x","visibility":"unlisted"}`)
|
||||
if v := getVis(t, s, resp["id"].(string)); v != "unlisted" {
|
||||
t.Fatalf("string field -> got %q, want unlisted", v)
|
||||
}
|
||||
resp = createPasteBody(t, s, `{"content":"y","visibility":"public"}`)
|
||||
if v := getVis(t, s, resp["id"].(string)); v != "public" {
|
||||
t.Fatalf("string field -> got %q, want public", v)
|
||||
}
|
||||
}
|
||||
|
||||
// TestPublicListExcludesPublicFalse: {"public":false} pastes stay out of /api/public.
|
||||
func TestPublicListExcludesPublicFalse(t *testing.T) {
|
||||
s := testServer(t)
|
||||
createPasteBody(t, s, `{"content":"hidden","public":false}`)
|
||||
req := httptest.NewRequest("GET", "/api/public", nil)
|
||||
rec := httptest.NewRecorder()
|
||||
s.routes().ServeHTTP(rec, req)
|
||||
var resp struct {
|
||||
Total int `json:"total"`
|
||||
}
|
||||
json.Unmarshal(rec.Body.Bytes(), &resp)
|
||||
if resp.Total != 0 {
|
||||
t.Fatalf("public:false paste leaked into /api/public: total=%d", resp.Total)
|
||||
}
|
||||
}
|
||||
@@ -48,8 +48,28 @@ func (l *limiter) allow(key string, rate, burst float64) bool {
|
||||
return true
|
||||
}
|
||||
|
||||
// clientIP extracts the request IP (no reverse proxy header by default).
|
||||
// clientIP extracts the client IP for rate-limit keying (#85).
|
||||
//
|
||||
// Trust boundary: palette runs behind exactly ONE trusted reverse proxy
|
||||
// (Traefik in the k3s pod network). Traefik APPENDS the real client IP to
|
||||
// X-Forwarded-For, so the RIGHTMOST entry is the last value the trusted
|
||||
// proxy observed and is unspoofable by the client (a client-supplied fake
|
||||
// entry only lands on the LEFT and is ignored). This matches chi's
|
||||
// middleware.RealIP semantics for a single trusted proxy hop.
|
||||
//
|
||||
// Direct connections (no XFF header) fall back to RemoteAddr. Directly
|
||||
// reachable deployments must NOT expose the app to untrusted networks
|
||||
// without a proxy in front, or attackers could forge the rightmost entry.
|
||||
func clientIP(r *http.Request) string {
|
||||
if xff := r.Header.Get("X-Forwarded-For"); xff != "" {
|
||||
if i := strings.LastIndex(xff, ","); i >= 0 {
|
||||
return strings.TrimSpace(xff[i+1:])
|
||||
}
|
||||
return strings.TrimSpace(xff)
|
||||
}
|
||||
if xr := r.Header.Get("X-Real-Ip"); xr != "" {
|
||||
return strings.TrimSpace(xr)
|
||||
}
|
||||
host := r.RemoteAddr
|
||||
if i := strings.LastIndex(host, ":"); i > 0 {
|
||||
host = host[:i]
|
||||
@@ -84,10 +104,16 @@ func rateLimitUnlock(id string, r *http.Request) bool {
|
||||
return globalLimiter.allow("unlock:"+id+":"+clientIP(r), 5.0/60.0, 5)
|
||||
}
|
||||
|
||||
// rateLimitAdmin: 5 attempts per minute per IP on the admin key check (#66),
|
||||
// same pattern as the unlock limiter (#34).
|
||||
func rateLimitAdmin(r *http.Request) bool {
|
||||
return globalLimiter.allow("admin:"+clientIP(r), 5.0/60.0, 5)
|
||||
}
|
||||
|
||||
// writeRateLimited responds 429 with Retry-After based on refill rate.
|
||||
func writeRateLimited(w http.ResponseWriter, retryAfterSecs int) {
|
||||
w.Header().Set("Retry-After", strconv.Itoa(retryAfterSecs))
|
||||
writeErr(w, 429, "rate limit exceeded")
|
||||
writeErrCode(w, 429, "rate_limited", "rate limit exceeded")
|
||||
}
|
||||
|
||||
// setRateLimitHeaders sets informational X-RateLimit headers for create/guess.
|
||||
|
||||
@@ -0,0 +1,85 @@
|
||||
package api
|
||||
|
||||
// Issue #85: the rate limit key must use the rightmost X-Forwarded-For entry
|
||||
// (appended by the trusted Traefik proxy), never the raw/leftmost header
|
||||
// value a client can forge. A spoofed FIRST XFF entry must not bypass the
|
||||
// limit or rotate buckets.
|
||||
|
||||
import (
|
||||
"bytes"
|
||||
"net/http/httptest"
|
||||
"testing"
|
||||
)
|
||||
|
||||
func TestClientIPTakesRightmostXFF(t *testing.T) {
|
||||
r := httptest.NewRequest("POST", "/", nil)
|
||||
r.RemoteAddr = "10.42.0.7:51000" // trusted Traefik pod
|
||||
r.Header.Set("X-Forwarded-For", "1.2.3.4, 1.2.3.5, 203.0.113.9")
|
||||
if got := clientIP(r); got != "203.0.113.9" {
|
||||
t.Fatalf("clientIP = %q, want rightmost 203.0.113.9", got)
|
||||
}
|
||||
}
|
||||
|
||||
func TestClientIPXRealIPFallback(t *testing.T) {
|
||||
r := httptest.NewRequest("POST", "/", nil)
|
||||
r.RemoteAddr = "10.42.0.7:51000"
|
||||
r.Header.Set("X-Real-Ip", "203.0.113.10")
|
||||
if got := clientIP(r); got != "203.0.113.10" {
|
||||
t.Fatalf("clientIP = %q, want 203.0.113.10", got)
|
||||
}
|
||||
}
|
||||
|
||||
func TestClientIPDirectFallback(t *testing.T) {
|
||||
r := httptest.NewRequest("POST", "/", nil)
|
||||
r.RemoteAddr = "198.51.100.5:51000"
|
||||
if got := clientIP(r); got != "198.51.100.5" {
|
||||
t.Fatalf("clientIP = %q, want 198.51.100.5", got)
|
||||
}
|
||||
}
|
||||
|
||||
// TestRateLimitSpoofedFirstXFFDoesNotBypass: an attacker rotating a fake
|
||||
// leftmost XFF entry stays limited on their real (rightmost) IP.
|
||||
func TestRateLimitSpoofedFirstXFFDoesNotBypass(t *testing.T) {
|
||||
srv := newTestServer(t)
|
||||
h := srv.routes()
|
||||
for i := 0; i < 5; i++ {
|
||||
req := httptest.NewRequest("POST", "/api/pastes", bytes.NewReader([]byte(`{"content":"hi"}`)))
|
||||
req.RemoteAddr = "10.42.0.7:51000"
|
||||
// each request spoofs a DIFFERENT leftmost entry
|
||||
req.Header.Set("X-Forwarded-For", spoofN(i)+", 203.0.113.9")
|
||||
rr := httptest.NewRecorder()
|
||||
h.ServeHTTP(rr, req)
|
||||
if rr.Code != 201 {
|
||||
t.Fatalf("req %d: want 201, got %d", i, rr.Code)
|
||||
}
|
||||
}
|
||||
// 6th request, still the same real IP, new spoofed prefix: must 429
|
||||
req := httptest.NewRequest("POST", "/api/pastes", bytes.NewReader([]byte(`{"content":"hi"}`)))
|
||||
req.RemoteAddr = "10.42.0.7:51000"
|
||||
req.Header.Set("X-Forwarded-For", "9.9.9.9, 203.0.113.9")
|
||||
rr := httptest.NewRecorder()
|
||||
h.ServeHTTP(rr, req)
|
||||
if rr.Code != 429 {
|
||||
t.Fatalf("spoofed 6th req: want 429, got %d", rr.Code)
|
||||
}
|
||||
}
|
||||
|
||||
func spoofN(i int) string {
|
||||
return "1.2.3." + string(rune('0'+i))
|
||||
}
|
||||
|
||||
// Distinct real IPs must still get distinct buckets (no over-limiting).
|
||||
func TestRateLimitDistinctRightmostIPsIndependent(t *testing.T) {
|
||||
srv := newTestServer(t)
|
||||
h := srv.routes()
|
||||
for _, ip := range []string{"203.0.113.20", "203.0.113.21"} {
|
||||
req := httptest.NewRequest("POST", "/api/pastes", bytes.NewReader([]byte(`{"content":"hi"}`)))
|
||||
req.RemoteAddr = "10.42.0.7:51000"
|
||||
req.Header.Set("X-Forwarded-For", "6.6.6.6, "+ip)
|
||||
rr := httptest.NewRecorder()
|
||||
h.ServeHTTP(rr, req)
|
||||
if rr.Code != 201 {
|
||||
t.Fatalf("ip %s: want 201, got %d", ip, rr.Code)
|
||||
}
|
||||
}
|
||||
}
|
||||
@@ -6,6 +6,7 @@ import (
|
||||
"context"
|
||||
"database/sql"
|
||||
"encoding/json"
|
||||
"errors"
|
||||
"fmt"
|
||||
"html/template"
|
||||
"net/http"
|
||||
@@ -51,6 +52,30 @@ func writeErr(w http.ResponseWriter, status int, msg string) {
|
||||
writeJSON(w, status, map[string]string{"error": msg})
|
||||
}
|
||||
|
||||
// writeErrCode emits a JSON error with a machine-readable code (#105): the
|
||||
// new-page JS maps known codes to plain-language messages, API consumers get
|
||||
// the stable `code` field alongside the human `error` text.
|
||||
func writeErrCode(w http.ResponseWriter, status int, code, msg string) {
|
||||
writeJSON(w, status, map[string]string{"error": msg, "code": code})
|
||||
}
|
||||
|
||||
// createErrCode maps a store.CreatePaste/CreateCan error to its UI error
|
||||
// code (#105).
|
||||
func createErrCode(err error) string {
|
||||
switch {
|
||||
case errors.Is(err, store.ErrSlugTaken):
|
||||
return "slug_taken"
|
||||
case errors.Is(err, store.ErrReservedSlug):
|
||||
return "slug_reserved"
|
||||
case errors.Is(err, store.ErrInvalidSlug):
|
||||
return "slug_invalid"
|
||||
case strings.Contains(err.Error(), "expires_in"):
|
||||
return "expiry_invalid"
|
||||
default:
|
||||
return "invalid_request"
|
||||
}
|
||||
}
|
||||
|
||||
// Routes returns the HTTP handler for the server.
|
||||
func (a *apiServer) Routes() http.Handler {
|
||||
return a.routes()
|
||||
@@ -60,7 +85,9 @@ func (a *apiServer) routes() http.Handler {
|
||||
r := chi.NewRouter()
|
||||
r.Use(middleware.Recoverer)
|
||||
r.Use(middleware.Timeout(30 * time.Second))
|
||||
r.Use(a.limitRequestBody) // #68: hard server-side body cap -> 413
|
||||
r.Use(viewerCookieMiddleware)
|
||||
r.Use(web.SecurityHeaders) // #59: CSP + hardening headers on HTML pages
|
||||
|
||||
// admin (#40): HTML page is open (key entry via form); API is key-guarded
|
||||
r.Get("/admin", a.ui.Handlers().HandleAdminPage)
|
||||
@@ -155,16 +182,47 @@ func (a *apiServer) handleCreatePaste(w http.ResponseWriter, r *http.Request) {
|
||||
}
|
||||
var p store.Paste
|
||||
if err := json.NewDecoder(r.Body).Decode(&p); err != nil {
|
||||
if isBodyTooLarge(err) { // #68: body cut off by MaxBytesReader
|
||||
writeErrCode(w, http.StatusRequestEntityTooLarge, "content_too_large", "request body too large")
|
||||
return
|
||||
}
|
||||
writeErr(w, 400, "invalid json body")
|
||||
return
|
||||
}
|
||||
if strings.TrimSpace(p.Content) == "" {
|
||||
writeErr(w, 400, "content is required")
|
||||
if status, msg := checkContent(p.Content, s.MaxContentBytes); status != 0 {
|
||||
if status == http.StatusRequestEntityTooLarge {
|
||||
writeErrCode(w, status, "content_too_large", msg)
|
||||
} else {
|
||||
writeErrCode(w, status, "content_empty", msg)
|
||||
}
|
||||
return
|
||||
}
|
||||
if int64(len(p.Content)) > s.MaxContentBytes { // #40: admin-tunable
|
||||
writeErr(w, 413, fmt.Sprintf("content exceeds max %d bytes", s.MaxContentBytes))
|
||||
return
|
||||
// #86: bound free-form metadata at create time
|
||||
if p.Title != nil {
|
||||
t, err := checkTitle(*p.Title)
|
||||
if err != nil {
|
||||
writeErr(w, 400, err.Error())
|
||||
return
|
||||
}
|
||||
p.Title = &t
|
||||
}
|
||||
if p.Language != nil {
|
||||
l, err := checkLanguage(*p.Language)
|
||||
if err != nil {
|
||||
writeErr(w, 400, err.Error())
|
||||
return
|
||||
}
|
||||
if l == "" {
|
||||
p.Language = nil
|
||||
} else {
|
||||
p.Language = &l
|
||||
}
|
||||
}
|
||||
if p.BurnAfterReads != nil { // #68: reject negative read budgets
|
||||
if err := parseBurnAfterReads(*p.BurnAfterReads); err != nil {
|
||||
writeErr(w, 400, err.Error())
|
||||
return
|
||||
}
|
||||
}
|
||||
// #40: admin-configurable default expiry
|
||||
if (p.ExpiresIn == nil || *p.ExpiresIn == "") && s.DefaultExpiry != "" {
|
||||
@@ -174,7 +232,7 @@ func (a *apiServer) handleCreatePaste(w http.ResponseWriter, r *http.Request) {
|
||||
p.ViewerID = currentViewerID(r)
|
||||
created, err := a.store.CreatePaste(&p)
|
||||
if err != nil {
|
||||
writeErr(w, 400, err.Error())
|
||||
writeErrCode(w, 400, createErrCode(err), err.Error())
|
||||
return
|
||||
}
|
||||
writeJSON(w, 201, map[string]any{
|
||||
@@ -209,6 +267,13 @@ func (a *apiServer) handleGetPaste(w http.ResponseWriter, r *http.Request) {
|
||||
return
|
||||
}
|
||||
if row.PasswordHash.Valid {
|
||||
// #81: every password verification (header, query param, or empty)
|
||||
// goes through the same per-IP+paste unlock limiter as the POST form
|
||||
// path, so brute-force via GET ?password= or X-Paste-Password gets 429.
|
||||
if !rateLimitUnlock(row.ID, r) {
|
||||
writeRateLimited(w, 60)
|
||||
return
|
||||
}
|
||||
// require password via header or query
|
||||
pw := r.Header.Get("X-Paste-Password")
|
||||
if pw == "" {
|
||||
@@ -293,11 +358,8 @@ func (a *apiServer) handleListMine(w http.ResponseWriter, r *http.Request) {
|
||||
writeJSON(w, 200, map[string]any{"total": 0, "items": []any{}})
|
||||
return
|
||||
}
|
||||
limit, _ := strconv.Atoi(r.URL.Query().Get("limit"))
|
||||
if limit <= 0 || limit > 100 {
|
||||
limit = 50
|
||||
}
|
||||
offset, _ := strconv.Atoi(r.URL.Query().Get("offset"))
|
||||
limit := parseLimit(r, 50, 100)
|
||||
offset := parseOffset(r)
|
||||
rows, total, err := a.store.ListMine(vid, limit, offset)
|
||||
if err != nil {
|
||||
writeErr(w, 500, "db error")
|
||||
@@ -317,11 +379,8 @@ func (a *apiServer) handleListMine(w http.ResponseWriter, r *http.Request) {
|
||||
}
|
||||
|
||||
func (a *apiServer) handleListPublic(w http.ResponseWriter, r *http.Request) {
|
||||
limit, _ := strconv.Atoi(r.URL.Query().Get("limit"))
|
||||
if limit <= 0 || limit > 100 {
|
||||
limit = 25
|
||||
}
|
||||
offset, _ := strconv.Atoi(r.URL.Query().Get("offset"))
|
||||
limit := parseLimit(r, 25, 100)
|
||||
offset := parseOffset(r)
|
||||
rows, total, err := a.store.ListPublic(limit, offset)
|
||||
if err != nil {
|
||||
writeErr(w, 500, "db error")
|
||||
|
||||
@@ -0,0 +1,136 @@
|
||||
package api
|
||||
|
||||
import (
|
||||
"errors"
|
||||
"fmt"
|
||||
"net/http"
|
||||
"regexp"
|
||||
"strconv"
|
||||
"strings"
|
||||
)
|
||||
|
||||
// #68 input-validation helpers. Paste/can payloads are size-capped and list
|
||||
// endpoints get a single place where limit/offset are parsed and clamped.
|
||||
|
||||
// maxRequestBody returns the HTTP body cap for JSON create endpoints: the
|
||||
// admin-tunable content cap plus headroom for JSON field overhead, floored
|
||||
// at 64KiB so a tiny admin-configured cap can't break small requests.
|
||||
func (a *apiServer) maxRequestBody() int64 {
|
||||
s := a.settings.get()
|
||||
max := s.MaxContentBytes + 4096
|
||||
if max < 64*1024 {
|
||||
max = 64 * 1024
|
||||
}
|
||||
return max
|
||||
}
|
||||
|
||||
// limitRequestBody wraps the request body with http.MaxBytesReader so
|
||||
// oversized payloads are cut off server-side instead of being fully decoded
|
||||
// into memory before the per-field size check runs (#68). A read over the
|
||||
// cap surfaces as *http.MaxBytesError, which handlers map to 413.
|
||||
func (a *apiServer) limitRequestBody(next http.Handler) http.Handler {
|
||||
return http.HandlerFunc(func(w http.ResponseWriter, r *http.Request) {
|
||||
if r.Body != nil {
|
||||
r.Body = http.MaxBytesReader(w, r.Body, a.maxRequestBody())
|
||||
}
|
||||
next.ServeHTTP(w, r)
|
||||
})
|
||||
}
|
||||
|
||||
// writeBodyTooLarge emits the 413 response for a body rejected by
|
||||
// MaxBytesReader.
|
||||
func writeBodyTooLarge(w http.ResponseWriter) {
|
||||
writeErr(w, http.StatusRequestEntityTooLarge, "request body too large")
|
||||
}
|
||||
|
||||
// isBodyTooLarge reports whether err came from http.MaxBytesReader.
|
||||
func isBodyTooLarge(err error) bool {
|
||||
var mbe *http.MaxBytesError
|
||||
return errors.As(err, &mbe)
|
||||
}
|
||||
|
||||
// checkContent validates paste content: rejects whitespace-only content
|
||||
// (400) and content over the byte cap (413). Returns (0, "") when valid.
|
||||
func checkContent(content string, maxBytes int64) (int, string) {
|
||||
if strings.TrimSpace(content) == "" {
|
||||
return http.StatusBadRequest, "content is required"
|
||||
}
|
||||
if int64(len(content)) > maxBytes { // #40/#68: admin-tunable cap
|
||||
return http.StatusRequestEntityTooLarge,
|
||||
fmt.Sprintf("content exceeds max %d bytes", maxBytes)
|
||||
}
|
||||
return 0, ""
|
||||
}
|
||||
|
||||
// parseLimit clamps the ?limit query param: missing/non-numeric/zero/negative
|
||||
// or over-max values fall back to def. Zero intentionally maps to the default
|
||||
// page size, matching the pre-existing `<= 0` clamp (#68).
|
||||
func parseLimit(r *http.Request, def, max int) int {
|
||||
n, err := strconv.Atoi(r.URL.Query().Get("limit"))
|
||||
if err != nil || n <= 0 || n > max {
|
||||
return def
|
||||
}
|
||||
return n
|
||||
}
|
||||
|
||||
// parseOffset clamps the ?offset query param: missing/non-numeric or negative
|
||||
// values become 0 (#68: negative offsets previously passed through to SQL).
|
||||
func parseOffset(r *http.Request) int {
|
||||
n, err := strconv.Atoi(r.URL.Query().Get("offset"))
|
||||
if err != nil || n < 0 {
|
||||
return 0
|
||||
}
|
||||
return n
|
||||
}
|
||||
|
||||
// parseBurnAfterReads validates the burn_after_reads field (#68): negative
|
||||
// values are rejected; zero/absent mean the default single read.
|
||||
func parseBurnAfterReads(n int) error {
|
||||
if n < 0 {
|
||||
return errors.New("burn_after_reads must be a positive number")
|
||||
}
|
||||
return nil
|
||||
}
|
||||
|
||||
// #86: bounds for free-form metadata fields on create.
|
||||
const (
|
||||
maxTitleLen = 200
|
||||
maxLanguageLen = 40
|
||||
)
|
||||
|
||||
// languageRe restricts language to identifiers like go, c#, f#, c++, objc.
|
||||
var languageRe = regexp.MustCompile(`^[a-zA-Z0-9+#-]{1,40}$`)
|
||||
|
||||
// checkTitle validates the paste title (#86): over-max titles are truncated
|
||||
// to 200 characters so a bloated listing entry can't be stored; whitespace
|
||||
// is trimmed first.
|
||||
func checkTitle(title string) (string, error) {
|
||||
title = strings.TrimSpace(title)
|
||||
if len(title) > maxTitleLen {
|
||||
return truncateRunes(title, maxTitleLen), nil
|
||||
}
|
||||
return title, nil
|
||||
}
|
||||
|
||||
// checkLanguage validates the language field (#86): optional, max 40 chars,
|
||||
// and must match ^[a-zA-Z0-9+#-]{1,40}$. Returns "" for absent/blank values.
|
||||
// Anything else malformed is a 400.
|
||||
func checkLanguage(lang string) (string, error) {
|
||||
lang = strings.TrimSpace(lang)
|
||||
if lang == "" {
|
||||
return "", nil
|
||||
}
|
||||
if len(lang) > maxLanguageLen || !languageRe.MatchString(lang) {
|
||||
return "", fmt.Errorf("language must match ^[a-zA-Z0-9+#-]{1,40}$ (max %d chars)", maxLanguageLen)
|
||||
}
|
||||
return lang, nil
|
||||
}
|
||||
|
||||
// truncateRunes cuts s to at most max runes, keeping the prefix intact.
|
||||
func truncateRunes(s string, max int) string {
|
||||
runes := []rune(s)
|
||||
if len(runes) <= max {
|
||||
return s
|
||||
}
|
||||
return string(runes[:max])
|
||||
}
|
||||
@@ -0,0 +1,121 @@
|
||||
package api
|
||||
|
||||
import (
|
||||
"net/http"
|
||||
"net/http/httptest"
|
||||
"strings"
|
||||
"testing"
|
||||
"time"
|
||||
|
||||
"palette/internal/store"
|
||||
)
|
||||
|
||||
// #95: HTML paste views dedupe per viewer (vwr cookie) within the burn viewer
|
||||
// window, reusing the paste_views table. Repeated views by the same viewer do
|
||||
// not inflate view_count; a different viewer counts.
|
||||
func TestHTMLViewsDedupedPerViewer(t *testing.T) {
|
||||
s := testServer(t)
|
||||
h := s.routes()
|
||||
|
||||
req := httptest.NewRequest("POST", "/api/pastes", strings.NewReader(`{"content":"vd"}`))
|
||||
rec := httptest.NewRecorder()
|
||||
h.ServeHTTP(rec, req)
|
||||
id := jsonField(t, rec.Body.String(), "id")
|
||||
|
||||
view := func(vwr string) {
|
||||
req := httptest.NewRequest("GET", "/"+id, nil)
|
||||
if vwr != "" {
|
||||
req.AddCookie(&http.Cookie{Name: "vwr", Value: vwr})
|
||||
}
|
||||
rec := httptest.NewRecorder()
|
||||
h.ServeHTTP(rec, req)
|
||||
if rec.Code != 200 {
|
||||
t.Fatalf("view: got %d", rec.Code)
|
||||
}
|
||||
}
|
||||
count := func() string {
|
||||
req := httptest.NewRequest("GET", "/api/pastes/"+id, nil)
|
||||
rec := httptest.NewRecorder()
|
||||
h.ServeHTTP(rec, req)
|
||||
return rec.Body.String()
|
||||
}
|
||||
|
||||
// same viewer (same cookie) renders twice: still 1 view
|
||||
view("v-a")
|
||||
view("v-a")
|
||||
if got := count(); !strings.Contains(got, `"view_count":1`) {
|
||||
t.Fatalf("expected view_count 1 after duplicate viewer views, got: %s", got)
|
||||
}
|
||||
// a different viewer counts
|
||||
view("v-b")
|
||||
if got := count(); !strings.Contains(got, `"view_count":2`) {
|
||||
t.Fatalf("expected view_count 2 after second viewer, got: %s", got)
|
||||
}
|
||||
// viewer without cookie counts every time (plain API clients, #49 decision)
|
||||
view("")
|
||||
view("")
|
||||
if got := count(); !strings.Contains(got, `"view_count":4`) {
|
||||
t.Fatalf("expected view_count 4 after uncoookied views, got: %s", got)
|
||||
}
|
||||
}
|
||||
|
||||
// #95: raw views always count, even from a cookie-holding viewer (#49 decision).
|
||||
func TestRawViewsAlwaysCount(t *testing.T) {
|
||||
s := testServer(t)
|
||||
h := s.routes()
|
||||
|
||||
req := httptest.NewRequest("POST", "/api/pastes", strings.NewReader(`{"content":"rv"}`))
|
||||
rec := httptest.NewRecorder()
|
||||
h.ServeHTTP(rec, req)
|
||||
id := jsonField(t, rec.Body.String(), "id")
|
||||
|
||||
for i := 0; i < 3; i++ {
|
||||
req := httptest.NewRequest("GET", "/raw/"+id, nil)
|
||||
req.AddCookie(&http.Cookie{Name: "vwr", Value: "same-viewer"})
|
||||
rec := httptest.NewRecorder()
|
||||
h.ServeHTTP(rec, req)
|
||||
if rec.Code != 200 {
|
||||
t.Fatalf("raw view: got %d", rec.Code)
|
||||
}
|
||||
}
|
||||
req = httptest.NewRequest("GET", "/api/pastes/"+id, nil)
|
||||
rec = httptest.NewRecorder()
|
||||
h.ServeHTTP(rec, req)
|
||||
if got := rec.Body.String(); !strings.Contains(got, `"view_count":3`) {
|
||||
t.Fatalf("expected view_count 3 after 3 raw views by one viewer, got: %s", got)
|
||||
}
|
||||
}
|
||||
|
||||
// #95: after the dedupe window passes, the same viewer counts again.
|
||||
func TestViewDedupeWindowExpires(t *testing.T) {
|
||||
s := testServer(t)
|
||||
h := s.routes()
|
||||
|
||||
req := httptest.NewRequest("POST", "/api/pastes", strings.NewReader(`{"content":"we"}`))
|
||||
rec := httptest.NewRecorder()
|
||||
h.ServeHTTP(rec, req)
|
||||
id := jsonField(t, rec.Body.String(), "id")
|
||||
|
||||
view := func() {
|
||||
req := httptest.NewRequest("GET", "/"+id, nil)
|
||||
req.AddCookie(&http.Cookie{Name: "vwr", Value: "v-w"})
|
||||
rec := httptest.NewRecorder()
|
||||
h.ServeHTTP(rec, req)
|
||||
if rec.Code != 200 {
|
||||
t.Fatalf("view: got %d", rec.Code)
|
||||
}
|
||||
}
|
||||
view()
|
||||
view()
|
||||
// jump past the 15-minute window
|
||||
realNow := store.TimeNow
|
||||
store.TimeNow = func() time.Time { return realNow().Add(16 * time.Minute) }
|
||||
defer func() { store.TimeNow = realNow }()
|
||||
view()
|
||||
req = httptest.NewRequest("GET", "/api/pastes/"+id, nil)
|
||||
rec = httptest.NewRecorder()
|
||||
h.ServeHTTP(rec, req)
|
||||
if got := rec.Body.String(); !strings.Contains(got, `"view_count":2`) {
|
||||
t.Fatalf("expected view_count 2 after window expiry, got: %s", got)
|
||||
}
|
||||
}
|
||||
@@ -211,13 +211,17 @@ func (s *Store) CreatePaste(p *Paste) (*Paste, error) {
|
||||
}
|
||||
}
|
||||
|
||||
// #49: burn-after-read pastes carry a read budget (default 1 read)
|
||||
if p.BurnAfterRead {
|
||||
// #49/#82: burn-after-read pastes carry a read budget (default 1 read).
|
||||
// burn_after_reads > 0 alone implies burn mode even without burn_after_read.
|
||||
if p.BurnAfterRead || (p.BurnAfterReads != nil && *p.BurnAfterReads > 0) {
|
||||
limit := int64(1)
|
||||
if p.BurnAfterReads != nil && *p.BurnAfterReads > 0 {
|
||||
limit = int64(*p.BurnAfterReads)
|
||||
}
|
||||
p.readsLimit = &limit
|
||||
if !p.BurnAfterRead {
|
||||
p.BurnAfterRead = true
|
||||
}
|
||||
}
|
||||
|
||||
visibility := p.Visibility
|
||||
|
||||
@@ -0,0 +1,46 @@
|
||||
package web
|
||||
|
||||
import (
|
||||
"net/http"
|
||||
"net/http/httptest"
|
||||
"testing"
|
||||
)
|
||||
|
||||
// #59: SecurityHeaders must add the CSP and hardening headers to rendered
|
||||
// HTML responses only; JSON and /raw responses pass through untouched.
|
||||
func TestSecurityHeaders(t *testing.T) {
|
||||
pages := http.HandlerFunc(func(w http.ResponseWriter, r *http.Request) {
|
||||
w.Header().Set("Content-Type", "text/html; charset=utf-8")
|
||||
w.Write([]byte("<html><body>ok</body></html>"))
|
||||
})
|
||||
h := SecurityHeaders(pages)
|
||||
rec := httptest.NewRecorder()
|
||||
h.ServeHTTP(rec, httptest.NewRequest("GET", "/", nil))
|
||||
wantCSP := "default-src 'self'; script-src 'self' 'unsafe-inline'; style-src 'self' 'unsafe-inline'; frame-ancestors 'none'"
|
||||
if got := rec.Header().Get("Content-Security-Policy"); got != wantCSP {
|
||||
t.Errorf("CSP = %q, want %q", got, wantCSP)
|
||||
}
|
||||
if got := rec.Header().Get("Referrer-Policy"); got != "no-referrer" {
|
||||
t.Errorf("Referrer-Policy = %q, want no-referrer", got)
|
||||
}
|
||||
if got := rec.Header().Get("X-Content-Type-Options"); got != "nosniff" {
|
||||
t.Errorf("X-Content-Type-Options = %q, want nosniff", got)
|
||||
}
|
||||
|
||||
// JSON/raw responses: headers are now set unconditionally BEFORE the handler
|
||||
// runs. The previous post-handler approach was silently dropped once a page
|
||||
// handler flushed its template output (headers must be set before WriteHeader).
|
||||
// CSP/nosniff/referrer on non-HTML bodies is harmless and desirable.
|
||||
jsonh := SecurityHeaders(http.HandlerFunc(func(w http.ResponseWriter, r *http.Request) {
|
||||
w.Header().Set("Content-Type", "application/json")
|
||||
w.Write([]byte(`{"ok":true}`))
|
||||
}))
|
||||
rec = httptest.NewRecorder()
|
||||
jsonh.ServeHTTP(rec, httptest.NewRequest("GET", "/api/x", nil))
|
||||
if got := rec.Header().Get("Content-Security-Policy"); got != wantCSP {
|
||||
t.Errorf("CSP missing on JSON response: got %q", got)
|
||||
}
|
||||
if got := rec.Header().Get("Referrer-Policy"); got != "no-referrer" {
|
||||
t.Errorf("Referrer-Policy missing on JSON response: got %q", got)
|
||||
}
|
||||
}
|
||||
@@ -143,7 +143,7 @@ body {
|
||||
/* paste view */
|
||||
.meta-bar { display: flex; align-items: center; gap: 12px; padding: 12px 18px; flex-wrap: wrap; }
|
||||
.meta-bar h1 { font-size: 29.2px; font-weight: 600; }
|
||||
.slug { font-family: var(--font-mono); font-size: 21.6px; color: var(--muted-fg); background: var(--surface-2); padding: 3px 9px; border-radius: var(--radius); }
|
||||
.slug { font-family: var(--font-mono); font-size: 21.6px; color: var(--muted-fg); background: var(--surface-2); padding: 3px 9px; border-radius: var(--radius-sm); }
|
||||
.tag { font-size: 19.8px; color: var(--muted-fg); border: 1px solid var(--border); border-radius: var(--radius-sm); padding: 2px 9px; }
|
||||
.paste-title-bar { display: flex; align-items: center; gap: 12px; padding: 12px 18px; flex-wrap: wrap; }
|
||||
.paste-title-bar h1 { font-size: 29.2px; font-weight: 600; margin: 0; }
|
||||
@@ -215,11 +215,8 @@ th {
|
||||
text-align: left; font-size: 18.9px; text-transform: uppercase; letter-spacing: .08em;
|
||||
color: var(--muted-fg); padding: 10px 16px; border-bottom: 1px solid var(--border); font-weight: 600;
|
||||
}
|
||||
/* #92: the sort-ind span is absolutely positioned in the cell's right gutter,
|
||||
so it can't shift the header label right of the data cells. */
|
||||
th.sortable { cursor: pointer; user-select: none; position: relative; padding-right: 34px; }
|
||||
th.sortable .sort-ind { position: absolute; right: 12px; top: 50%; transform: translateY(-50%); margin-left: 0; }
|
||||
td { padding: 10px 16px; border-bottom: 1px solid var(--border); overflow: hidden; text-overflow: ellipsis; white-space: nowrap; }
|
||||
td { padding: 10px 16px; border-bottom: 1px solid var(--border); overflow: clip; text-overflow: ellipsis; white-space: nowrap; }
|
||||
td:has(> a.slug), td:has(> .slug) { overflow: visible; }
|
||||
tr:last-child td { border-bottom: none; }
|
||||
tr.row { cursor: pointer; }
|
||||
tr.row:hover td { background: var(--surface-2); }
|
||||
@@ -299,6 +296,13 @@ td a.slug:hover { color: var(--accent); }
|
||||
.toast.success { border-color: var(--ok); color: var(--ok); }
|
||||
.toast.error { border-color: var(--err); color: var(--err); }
|
||||
|
||||
/* result box color-coding (#105): colored left border + text tint per status */
|
||||
.result-ok, .result-err, .result-warn { border-left: 4px solid transparent; padding-left: 10px; }
|
||||
.result-ok { border-left-color: var(--ok); color: var(--ok); }
|
||||
.result-err { border-left-color: var(--err); color: var(--err); }
|
||||
.result-warn { border-left-color: var(--warn); color: var(--warn); }
|
||||
.result-ok a { color: var(--ok); }
|
||||
|
||||
/* protection section rhythm (#20) */
|
||||
.protect { display: flex; flex-direction: column; gap: 2px; }
|
||||
.protect .pw-row { padding: 2px 8px 4px; }
|
||||
@@ -351,17 +355,29 @@ td a.slug:hover { color: var(--accent); }
|
||||
/* paste name under slug pill in Paste column (#43) */
|
||||
.paste-sub { font-size: 19.8px; color: var(--muted-fg); margin-top: 2px; overflow: hidden; text-overflow: ellipsis; white-space: nowrap; }
|
||||
.paste-sub.dim { color: var(--muted); }
|
||||
td .url-link { font-size: 19.8px; }
|
||||
td a.slug.url-link { max-width: 100%; display: inline-block; vertical-align: middle; overflow: hidden; text-overflow: ellipsis; white-space: nowrap; box-sizing: border-box; }
|
||||
td .id-link { color: var(--muted-fg); text-decoration: none; font-family: var(--font-mono); font-size: 19.8px; }
|
||||
td .id-link:hover { color: var(--accent); }
|
||||
|
||||
/* sortable column headers (#42) */
|
||||
th.sortable { cursor: pointer; user-select: none; }
|
||||
th.sortable:hover { color: var(--fg); }
|
||||
.sort-ind { display: inline-block; width: 0; height: 0; margin-left: 6px; vertical-align: middle; border-left: 5px solid transparent; border-right: 5px solid transparent; }
|
||||
th.sortable { cursor: pointer; user-select: none; white-space: nowrap; }
|
||||
/* #101: arrow sits LEFT of the label, further spaced, vertically centered,
|
||||
and absolutely positioned so it never shifts the label text. */
|
||||
th.sortable { position: relative; padding-left: 24px; }
|
||||
th.sortable .sort-ind {
|
||||
position: absolute; left: 8px; top: 50%; transform: translateY(-50%);
|
||||
display: inline-block; width: 0; height: 0;
|
||||
border-left: 5px solid transparent; border-right: 5px solid transparent;
|
||||
}
|
||||
th.sorted.asc .sort-ind { border-bottom: 6px solid var(--accent); }
|
||||
th.sorted.desc .sort-ind { border-top: 6px solid var(--accent); }
|
||||
|
||||
/* #102: small unobtrusive admin link on the settings page */
|
||||
a.admin-link { color: var(--muted-fg); font-size: 15px; text-decoration: none; }
|
||||
a.admin-link:hover { color: var(--fg); text-decoration: underline; }
|
||||
|
||||
/* ============================================================
|
||||
Consistency audit (#18) — shared tokens across inputs, buttons,
|
||||
headings. Visual-only, no behavior change.
|
||||
|
||||
@@ -63,7 +63,7 @@ const PaletteTable = (() => {
|
||||
const filtered = state.filter.length > 0;
|
||||
const off = (state.page - 1) * opts.perPage;
|
||||
const url = (filtered || state.sortKey)
|
||||
? opts.endpoint + '?limit=500&offset=0'
|
||||
? opts.endpoint + '?limit=' + (opts.fetchLimit || 100) + '&offset=0'
|
||||
: opts.endpoint + '?limit=' + opts.perPage + '&offset=' + off;
|
||||
const res = await fetch(url);
|
||||
const data = await res.json();
|
||||
|
||||
@@ -44,7 +44,8 @@
|
||||
|
||||
function api(path, opts) {
|
||||
opts = opts || {};
|
||||
opts.headers = { 'X-Admin-Key': key() };
|
||||
// allow callers to override the key header (e.g. validating a typed key, #99)
|
||||
opts.headers = Object.assign({ 'X-Admin-Key': key() }, opts.headers || {});
|
||||
if (opts.body) opts.headers['Content-Type'] = 'application/json';
|
||||
return fetch(path, opts);
|
||||
}
|
||||
@@ -72,9 +73,10 @@
|
||||
|
||||
document.getElementById('admin-key-form').addEventListener('submit', function (e) {
|
||||
e.preventDefault();
|
||||
sessionStorage.setItem(KEY, keyInput.value);
|
||||
api('/admin/api/settings').then(function (r) {
|
||||
// #99: don't persist the key until the server accepts it
|
||||
api('/admin/api/settings', { headers: { 'X-Admin-Key': keyInput.value } }).then(function (r) {
|
||||
if (r.status === 200) {
|
||||
sessionStorage.setItem(KEY, keyInput.value);
|
||||
status.textContent = '✓';
|
||||
keyInput.value = '';
|
||||
loadSettings();
|
||||
@@ -101,7 +103,9 @@
|
||||
});
|
||||
});
|
||||
|
||||
if (key()) loadSettings();
|
||||
// #112: always show the lock on fresh load — do not auto-restore the
|
||||
// panel from a stale sessionStorage key. The key is only written after a
|
||||
// successful unlock (above) so in-page actions still work within this visit.
|
||||
})();
|
||||
</script>
|
||||
{{template "foot" .}}
|
||||
|
||||
@@ -3,9 +3,10 @@
|
||||
<meta name="viewport" content="width=device-width, initial-scale=1">
|
||||
<link rel="stylesheet" href="/static/app.css">
|
||||
<script>
|
||||
// preset preview hook (#16): ?theme=<name> sets data-preset for screenshots only
|
||||
// preset hook (#16): ?theme= wins; else persisted choice (#100)
|
||||
(function () {
|
||||
var t = new URLSearchParams(location.search).get('theme');
|
||||
if (!t) try { t = localStorage.getItem('palette-theme'); } catch (e) {}
|
||||
if (t) document.documentElement.dataset.preset = t;
|
||||
})();
|
||||
</script>
|
||||
@@ -13,7 +14,7 @@
|
||||
|
||||
{{define "topbar"}}
|
||||
<div class="topbar">
|
||||
<a class="logo" href="/history">Palette <em>/ beta</em></a>
|
||||
<a class="logo" href="/history">Palette <em>/ {{ version }}</em></a>
|
||||
<nav>
|
||||
<a href="/new" {{if eq .Page "new"}}class="on"{{end}}>New</a>
|
||||
<a href="/history" {{if eq .Page "history"}}class="on"{{end}}>Public</a>
|
||||
|
||||
@@ -171,10 +171,37 @@ $('can-add').addEventListener('click', addCanItem);
|
||||
|
||||
let guessed = ''; // last auto-detected language, '' = user override
|
||||
|
||||
function showResult(html, isError) {
|
||||
// #105: map backend machine-readable error codes to plain-language guidance.
|
||||
// Unknown codes fall back to a generic message; the technical detail stays
|
||||
// in the API response for API consumers.
|
||||
const ERROR_MESSAGES = {
|
||||
slug_taken: 'That Custom URL is already taken. Try another.',
|
||||
slug_reserved: 'That Custom URL is reserved. Try another.',
|
||||
slug_invalid: 'Please keep the Custom URL under 64 characters, using only letters, numbers, dashes, or underscores.',
|
||||
content_empty: 'Write or paste something first.',
|
||||
content_too_large: 'This paste is too large. The limit is 5 MB.',
|
||||
expiry_invalid: 'Please pick an expiry between 1 minute and 1 year.',
|
||||
rate_limited: 'Too many tries. Wait a minute and try again.',
|
||||
};
|
||||
const GENERIC_ERROR = 'Something went wrong. Please try again.';
|
||||
|
||||
function friendlyError(data) {
|
||||
return ERROR_MESSAGES[data && data.code] || GENERIC_ERROR;
|
||||
}
|
||||
|
||||
// #105: color the result box by outcome — success (ok), error (err),
|
||||
// warning (warn) — with a colored left border (CSS .result-ok/.result-err).
|
||||
function setResultKind(kind) {
|
||||
const card = $('result-card');
|
||||
card.classList.remove('result-ok', 'result-err', 'result-warn');
|
||||
if (kind) card.classList.add('result-' + kind);
|
||||
}
|
||||
|
||||
function showResult(html, kind) {
|
||||
$('result').innerHTML = html;
|
||||
$('result').dataset.token = isError ? '' : ($('result').dataset.token || '');
|
||||
$('result').dataset.token = kind === 'ok' ? ($('result').dataset.token || '') : ($('result').dataset.token || '');
|
||||
$('result-card').style.display = 'block';
|
||||
setResultKind(kind === 'ok' ? 'ok' : (kind === 'warn' ? 'warn' : 'err'));
|
||||
}
|
||||
function defaultFilename(lang) {
|
||||
const names = {
|
||||
@@ -249,12 +276,12 @@ async function create() {
|
||||
});
|
||||
const data = await res.json();
|
||||
if (!res.ok) {
|
||||
showResult('Error: ' + (data.error || res.status), true);
|
||||
showResult(friendlyError(data), 'err');
|
||||
toast('Create failed', 'error');
|
||||
return;
|
||||
}
|
||||
const url = location.origin + '/' + (data.custom_slug || data.id);
|
||||
showResult('<a href="' + url + '">' + url + '</a> <button class="btn btn-icon" id="result-copy" title="Copy URL" type="button">⧉</button>', false);
|
||||
showResult('<a href="' + url + '">' + url + '</a> <button class="btn btn-icon" id="result-copy" title="Copy URL" type="button">⧉</button>', 'ok');
|
||||
$('result').dataset.token = data.deletion_token || '';
|
||||
const copyBtn = document.getElementById('result-copy');
|
||||
copyBtn.addEventListener('click', () => {
|
||||
@@ -312,12 +339,12 @@ async function createCan() {
|
||||
const res = await fetch('/api/pastes/can', {method: 'POST', body: fd});
|
||||
const data = await res.json();
|
||||
if (!res.ok) {
|
||||
showResult('Error: ' + (data.error || res.status), true);
|
||||
showResult(friendlyError(data), 'err');
|
||||
toast('Can create failed', 'error');
|
||||
return;
|
||||
}
|
||||
const url = location.origin + data.url;
|
||||
showResult('<a href="' + url + '">' + url + '</a> <button class="btn btn-icon" id="result-copy" title="Copy URL" type="button">⧉</button>', false);
|
||||
showResult('<a href="' + url + '">' + url + '</a> <button class="btn btn-icon" id="result-copy" title="Copy URL" type="button">⧉</button>', 'ok');
|
||||
const copyBtn = document.getElementById('result-copy');
|
||||
copyBtn.addEventListener('click', () => {
|
||||
try {
|
||||
|
||||
@@ -6,8 +6,55 @@
|
||||
<h1>Settings</h1>
|
||||
</div>
|
||||
<div class="settings-body">
|
||||
<p>Settings are under construction.</p>
|
||||
<h3>Theme</h3>
|
||||
<div class="theme-grid" id="theme-grid"></div>
|
||||
<p class="admin-link-row"><a class="admin-link" href="/admin">Admin</a></p>
|
||||
</div>
|
||||
</div>
|
||||
</div>
|
||||
<script>
|
||||
(function () {
|
||||
// #112: derive each preset's swatches from the real CSS variables in
|
||||
// app.css by temporarily applying data-preset, so they can never drift.
|
||||
var themeNames = [
|
||||
{ id: 'midnight', name: 'Midnight' },
|
||||
{ id: 'smooth', name: 'Smooth' },
|
||||
{ id: 'pastel-lavender', name: 'Pastel Lavender' },
|
||||
{ id: 'pastel-peach', name: 'Pastel Peach' },
|
||||
{ id: 'pastel-cloud', name: 'Pastel Cloud' }
|
||||
];
|
||||
var SWATCH_VARS = ['--bg', '--surface', '--surface-2', '--muted', '--accent'];
|
||||
|
||||
function presetColors(id) {
|
||||
var root = document.documentElement;
|
||||
var prev = root.getAttribute('data-preset');
|
||||
root.setAttribute('data-preset', id);
|
||||
var cs = getComputedStyle(root);
|
||||
var colors = SWATCH_VARS.map(function (v) { return cs.getPropertyValue(v).trim(); });
|
||||
if (prev === null) root.removeAttribute('data-preset'); else root.setAttribute('data-preset', prev);
|
||||
return colors;
|
||||
}
|
||||
|
||||
var grid = document.getElementById('theme-grid');
|
||||
var current = document.documentElement.dataset.preset || 'midnight';
|
||||
themeNames.forEach(function (t) {
|
||||
var colors = presetColors(t.id);
|
||||
var btn = document.createElement('button');
|
||||
btn.type = 'button';
|
||||
btn.className = 'theme-card';
|
||||
btn.setAttribute('aria-pressed', current === t.id ? 'true' : 'false');
|
||||
btn.innerHTML = '<strong>' + t.name + '</strong>' +
|
||||
'<span class="swatches">' + colors.map(function (c) {
|
||||
return '<span class="swatch" style="background:' + c + '"></span>';
|
||||
}).join('') + '</span>';
|
||||
btn.addEventListener('click', function () {
|
||||
document.documentElement.dataset.preset = t.id;
|
||||
try { localStorage.setItem('palette-theme', t.id); } catch (e) {}
|
||||
grid.querySelectorAll('.theme-card').forEach(function (c) { c.setAttribute('aria-pressed', 'false'); });
|
||||
btn.setAttribute('aria-pressed', 'true');
|
||||
});
|
||||
grid.appendChild(btn);
|
||||
});
|
||||
})();
|
||||
</script>
|
||||
{{template "foot" .}}
|
||||
|
||||
@@ -0,0 +1,6 @@
|
||||
package web
|
||||
|
||||
// Version is the display version, set at build time via
|
||||
// -ldflags "-X palette/internal/web.Version=v0.2.1" (#93). Falls back to
|
||||
// "dev" for bare `go build` runs.
|
||||
var Version = "dev"
|
||||
@@ -328,3 +328,25 @@ func (h *Handlers) HandleAdminPage(w http.ResponseWriter, r *http.Request) {
|
||||
|
||||
// Handlers builds a web.Handlers bound to this UI.
|
||||
func (u *UI) Handlers() *Handlers { return &Handlers{UI: u} }
|
||||
|
||||
// #59: security headers for rendered HTML pages. Applied wherever the
|
||||
// response is text/html (page templates and the inline can page); JSON API
|
||||
// responses and /raw content pass through untouched. script-src allows
|
||||
// 'unsafe-inline' because the page templates carry inline scripts; CSP
|
||||
// default-src 'self' still blocks external content and object/frame embeds,
|
||||
// and frame-ancestors 'none' closes the clickjacking gap flagged in the #34
|
||||
// pentest. Runs after the handler so the Content-Type is already set.
|
||||
func SecurityHeaders(next http.Handler) http.Handler {
|
||||
return http.HandlerFunc(func(w http.ResponseWriter, r *http.Request) {
|
||||
// Set before the handler runs: once a handler writes (template render
|
||||
// flushes), header mutations are silently dropped. Setting the headers
|
||||
// unconditionally is safe: CSP/nosniff/referrer on JSON or /raw bodies
|
||||
// is harmless and arguably desirable.
|
||||
h := w.Header()
|
||||
h.Set("Content-Security-Policy",
|
||||
"default-src 'self'; script-src 'self' 'unsafe-inline'; style-src 'self' 'unsafe-inline'; frame-ancestors 'none'")
|
||||
h.Set("Referrer-Policy", "no-referrer")
|
||||
h.Set("X-Content-Type-Options", "nosniff")
|
||||
next.ServeHTTP(w, r)
|
||||
})
|
||||
}
|
||||
|
||||